Browse categories
Explore
Fiverr Pro
English
$
USD
I find and fix real security bugs in web applications, APIs, and WordPress plugins, and I hand you a clear report plus working fixes, not a scary PDF you cannot act on.
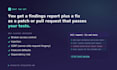
What you get: every finding with the exact location, why it is exploitable, and how to fix it, then the fix itself as a patch or pull request that builds and passes your tests.
I focus on the bugs that actually matter: broken access control and authorization, injection, SSRF, insecure defaults, and dependency risks. My open-source security work is public at research.itsjustin.me.
This is authorized, defensive security only. I review code you own or are clearly authorized to have reviewed. I do not attack live systems or third-party targets.
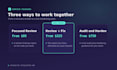
Message me first with your stack and roughly how large the codebase is, and I will tell you honestly which package fits and what I can commit to.

Development technology:
JavaScript
Do you test against my live site?
No. I do a static review of your source and deliver fixes. Any dynamic testing happens only if you authorize it in writing and it is your own system.
What do I get at the end?
A findings report with the exact location and severity of each issue, plus fixes delivered as a patch or pull request that builds and passes your tests, on the Review and Fix and Audit and Harden packages.
Which languages and stacks do you cover?
JavaScript and TypeScript, Python, PHP and WordPress, and Go.
Will you sign an NDA?
Yes, on request.


