Browse categories
Explore
Fiverr Pro
English
$
USD


Is your API leaking data or letting users access things they shouldn't? Find out before someone else does.
I test REST and GraphQL APIs for real security weaknesses and give you a clear report your developers can act on.
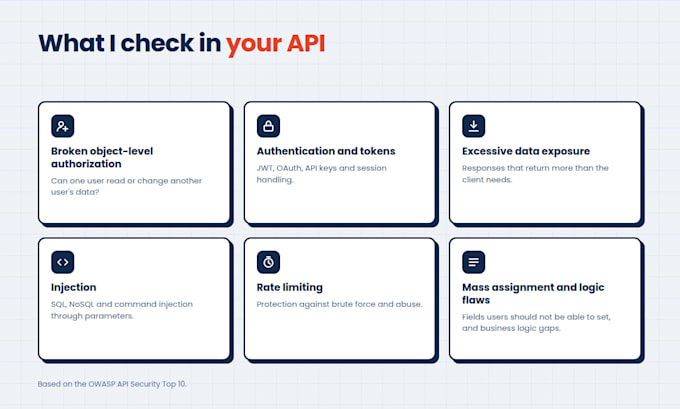
WHAT I CHECK
- Broken object-level authorization (can one user access another user's data?)
- Authentication and token handling (JWT, OAuth, API keys)
- Excessive data exposure in responses
- Injection flaws (SQL, NoSQL, command)
- Rate limiting and brute-force protection
- Mass assignment and business logic flaws
WHAT YOU GET
- PDF report with findings ranked by severity
- Step-by-step reproduction for each issue
- Plain-language fix recommendations
- Free retest after you apply fixes (Full and Deep packages)
HOW IT WORKS
1. You send API documentation (Postman collection, OpenAPI/Swagger file, or endpoint list) and test accounts.
2. We agree on scope and testing window.
3. I test using manual techniques and trusted tools.
4. You receive the report and I answer your questions.
I only test APIs you own or are authorized to test, in a staging environment where possible. Your findings stay confidential.
Message me before ordering for large or complex APIs.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Cybersecurity Professional
Languages