Browse categories
English
$
USD
Connect to your AI
Network Cloud Security Engineer, SOC Engineer, Ethical Hacker
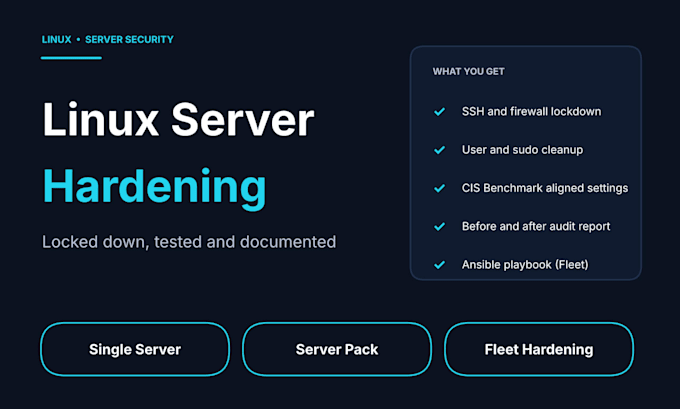
Is your Linux server running on default settings? I harden servers as a SOC engineer, so I know what attackers try first. Ill lock yours down, check that nothing breaks, and give you a clear before-and-after report.
WHAT I DO
SUPPORTED SYSTEMS
Ubuntu, Debian and RHEL-based servers (Rocky, AlmaLinux, CentOS).
HOW IT WORKS
Message me first with your setup. I work in a maintenance window or on a copy so your services stay up, and I explain every change I make.
Higher packages add more servers, a reusable Ansible playbook and a handover call.
Operating system:
Linux
Will hardening break my services?
I work in a maintenance window or on a copy, change things in small steps, and test after each one. If a change risks breaking something, I ask first.
What access do you need?
SSH access with sudo, using temporary credentials or keys you can revoke afterward. Never send passwords in chat.
Do you guarantee my server will be secure?
No one can. You get a hardened configuration that closes the most common attack paths, plus a report showing exactly what changed.
