Browse categories
Explore
Fiverr Pro
English
$
USD
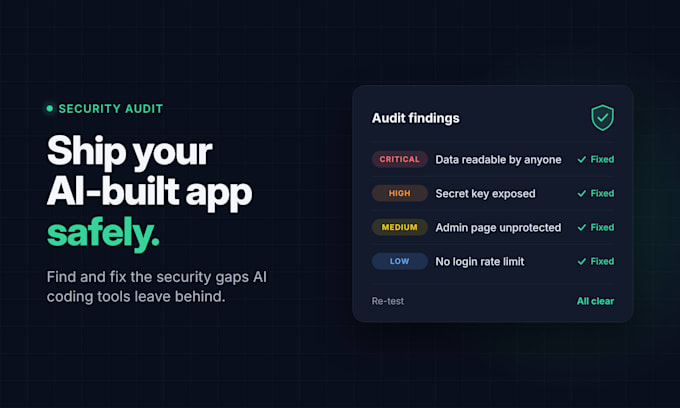
Built your app with Lovable, Bolt, Replit, Cursor, or Claude Code and about to launch, take payments, or raise? I find and fix the security holes AI tools leave behind.
What I check:
What you get: a report ranked by severity in plain English, fixes as pull requests (Premium), and a re-test to confirm everything is closed.
5+ years building and fixing Next.js + Supabase apps, with 90+ client projects delivered.
AI engineer and security reviewer for AI built apps
Languages
Do you need access to my code?
Yes. I need the live app URL, a test login for each user role, and read access to your repo. Code access is what lets me find issues a quick outside scan would miss.
Will you change my code?
Only in the Premium package, where fixes come as pull requests you review and merge. Basic and Standard give you the findings with clear fix steps your team can follow.
Which tools and stacks do you cover?
Apps built with Lovable, Bolt, Replit, Cursor, Claude Code, or by hand, on Next.js, React, Supabase, Firebase, Postgres, Clerk, Auth0, and Stripe. Message me if your stack isn't listed.
