Browse categories
Explore
Fiverr Pro
English
$
USD
Can one customer see another customer's data? Can a regular user reach an admin action by changing an ID in a request? Automated scanners rarely catch this. It's the most common serious flaw in web apps, and it's what I test for.
I've written access-control tests on a HIPAA-compliant telehealth platform, confirming that each user role can reach only the patient data it's allowed to see. I'm a full-stack developer on Django, Next.js and PostgreSQL, so I read your app as its builder would.
What I check, by hand, with test accounts you provide:
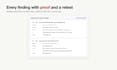
You get a report listing each issue with its severity, the exact steps to reproduce it, and how to fix it.
Tell me about your app and its user roles, and I'll confirm the scope.

Testing application:
API
Development technology:
Django
•
Node.js
•
Python
•
React
•
TypeScript
Device:
PC
•
Mac
Do you test my live site?
Only a staging copy or an environment you own and authorize in writing, with test accounts you create.
How is this different from a penetration test?
It goes deep on one area: who can see and change what in your app. Every finding is checked by hand with real test accounts.


