Browse categories
English
$
USD
Connect to your AI
Backend and DevOps Developer, Linux Server Security and Cloudflare
Is your Linux server open to brute-force logins and bots? I will lock it down with a clear, tested checklist, without breaking your running apps.
What I do:
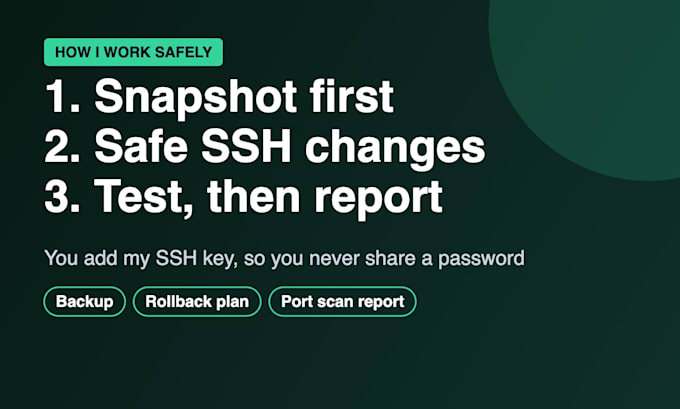
How I keep your server safe while I work: I ask for a snapshot or backup first, keep a second SSH session open while changing SSH and firewall rules, and test the new login before closing anything. You never send me a password: you add my public SSH key and remove it when we are done.
You get a short report of what was changed, with a before and after open-port scan.
Works with Ubuntu and Debian on any VPS: Hetzner, DigitalOcean, AWS EC2, Linode, Contabo and others.
Please message me before ordering with your server OS and the apps it runs.
Operating system:
Linux
Will my website go down?
No planned downtime for most jobs. If a reboot is needed for updates, I agree the time with you first.
What access do you need?
A sudo user. You add my public SSH key, so you never share a password, and you remove the key after delivery.
What if something goes wrong?
I work with a backup or snapshot and keep a second SSH session open, so any change can be rolled back. Console access from your hosting provider is the final fallback.
Do you support Windows or cPanel servers?
No. This gig covers Ubuntu and Debian servers without cPanel. Message me if you are not sure.
Is this a penetration test?
No. This is hardening: securing your server settings. It is not a penetration test or a full security audit.