Browse categories
English
$
USD
Connect to your AI
Cloud Security Architect focused on AWS and the Cloudflare edge
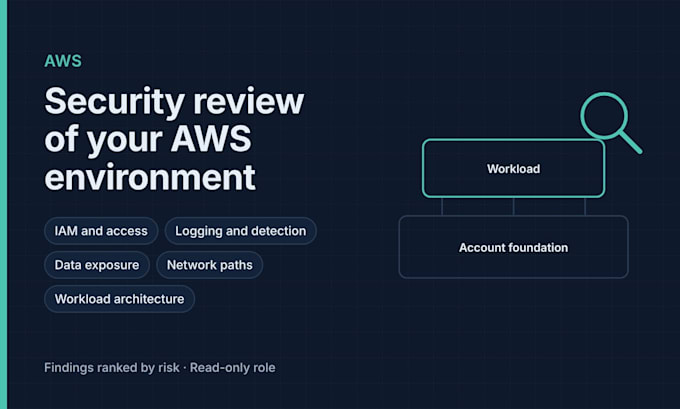
A security review of your AWS environment by an AWS-certified security architect, covering two layers.
Account foundation, common to every business: root and IAM access, MFA and SSO, CloudTrail and Config, GuardDuty and Security Hub, public S3 and snapshot exposure, encryption defaults, network defaults and organisation guardrails.
Workload, specific to your application: how your services, data, network paths, secrets and IAM roles fit together, and where an attacker would get in.
What you get: a report with a one-page summary, findings ranked by risk and business impact, and clear steps to fix them. I use a read-only role that you can delete at any time.
Which package? Count your AWS accounts and the applications you want reviewed. One large account running several applications is one account plus several workloads.
Not included: changes to your environment (see my hardening gigs), penetration testing, application code review.
Cloud provider:
Amazon Web Services
Expertise:
Installation
•
Backup
•
Debugging
•
Development
•
Configuration
Cloud computing resource:
ELB
•
Route53
•
VPC
•
Security Groups
•
DNS
What exactly do I receive?
A PDF report: a one-page summary in plain English, then each finding with its risk level, what it means for your business and how to fix it. Hardening orders also include a change log listing every change and how to reverse it.
What access do you need, and is it safe?
Read-only access for audits, created with step-by-step instructions I send you. I never ask for passwords, root access or personal logins, and you can remove my access the moment the work is done.
Which package should I choose?
AWS: count your accounts and the applications in scope. If you are unsure, message me and I will recommend one.
Will this cause downtime?
Audits are read-only and change nothing. For hardening, every change is agreed with you first and applied in stages, and anything that could block real users is introduced gradually.
When does the delivery time start?
When your requirements and access are in place. If access is delayed, I will ask for a short extension rather than rush the work.
Do you do penetration testing?
No. I review and improve configuration and architecture. I do not attack or exploit your systems.
Can you fix the issues you find?
Yes, through my hardening gigs. If you order hardening within 30 days of an audit, I credit half of the audit price through a custom offer.
How do you handle my data?
I only read configuration, never copy your business data, keep findings encrypted and delete them 30 days after delivery. I can sign a reasonable NDA.
Can you help with an active security incident?
Message me first. Whether I can help depends on the situation and my availability at the time, so I cannot guarantee response times for incidents.
Do you offer ongoing support?
Yes. After a first project, I can offer a monthly arrangement for configuration reviews and questions as your setup changes.
