Browse categories
English
$
USD
Connect to your AI

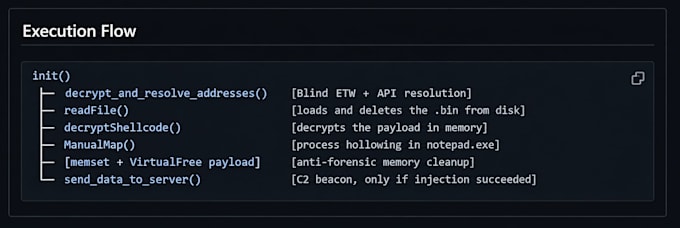
Have you detected a suspicious file on your system or network? I perform forensic analysis of Windows malware, identifying its behavior, persistence mechanisms, capabilities, and indicators of compromise (IOCs) you can use to protect your environment.
I work with real samples in an isolated, controlled environment, following forensic procedures that guarantee evidence integrity.
What I offer:
Languages
How do I send you the sample?
Use a password-protected ZIP and share the password separately. I’ll provide secure upload instructions.
Do you analyze ransomware?
Yes, but I do not decrypt files. I focus on behavior and IOCs.
Can you tell me if my system is infected?
I analyze the sample, not your system. But I can provide guidance on containment.
Is the report usable for legal purposes?
I follow forensic methodology, but I’m not a certified legal expert. The report is technical.
Do you modify the malware?
No. I only analyze it defensively.
