Browse categories
Explore
Fiverr Pro
English
$
USD
Turn raw log data into clear, actionable SPL searches.
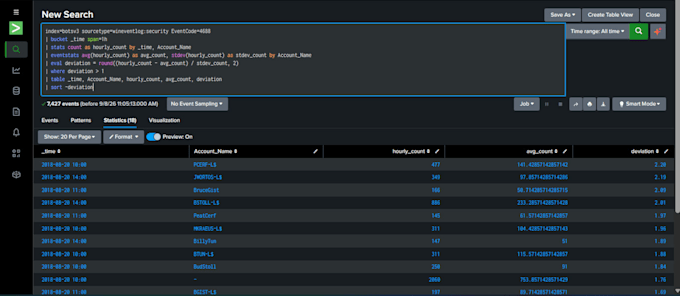
I write and optimize Splunk SPL queries to help you search, filter, and make sense of large volumes of log data, whether that's narrowing a huge dataset to specific events, extracting key fields, or building a reusable search for ongoing monitoring.
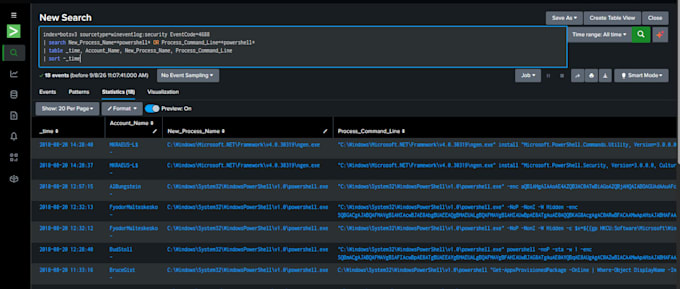
Example of my work: Using Windows Security event logs, I built a search to hunt for suspicious PowerShell activity, surfacing process execution events using encoded or hidden-window flags, a common technique used to hide malicious activity. It returned 18 relevant events out of thousands, cutting straight to what actually needs investigating.
What I can do:
Before ordering, have ready:
Let's turn your logs into answers.
Do I need to give you access to my Splunk instance?
Yes, or you can send sample/exported log data instead
What log sources can you work with?
Most standard logs ingested into Splunk, security logs, system events, process activity, network logs, and more
Will the search work long-term, or is it one-time use?
Standard and Premium queries are built to be reusable, not just a one-off answer.
Can you write searches for threat hunting, not just basic filtering?
Yes, I can build searches around specific indicators, patterns, or suspicious behavior, like the PowerShell example in my gig.