Browse categories
English
$
USD
Connect to your AI


Hello and welcome! Thanks for stopping by.
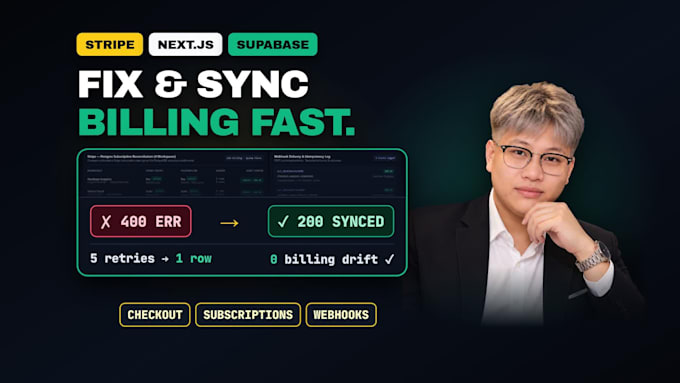
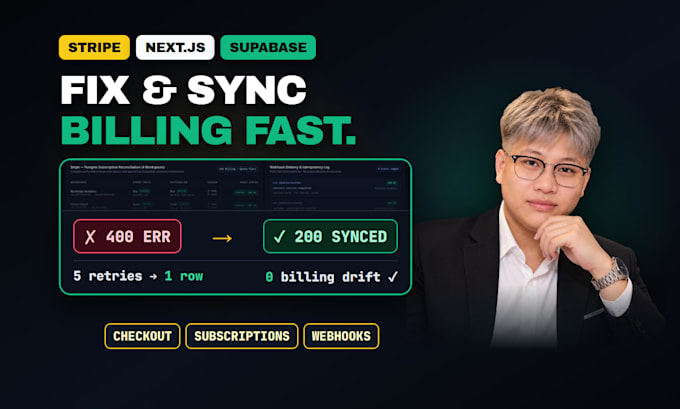
Did a user pay in Stripe, yet your Next.js, React or Supabase app never upgraded their plan? Seeing webhook HTTP 400 errors, duplicate rows, or broken billing in Lovable or Bolt?
I read your server code, verify raw webhook signatures and lock each event in a database transaction, proved before and after.
What I fix and build:
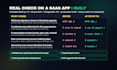
Real result on a SaaS app I built (production build): webhook HTTP 400 to 200, 5 retries wrote 1 ledger row (0 duplicates), 0 leaked client keys.
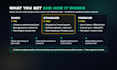
What you get:
I never need your passwords, live secret keys or card data.
Need something not listed here? Message me before you order for a free first check and a custom offer!
Full Stack Web Developer, Nextjs, Supabase, Stripe and AI Web Apps
Languages
What exactly do you fix or integrate in Stripe?
I fix broken webhooks (HTTP 400 signature errors, middleware 307 redirects, duplicate retry writes) and build clean Stripe Checkout, Subscriptions, Customer Billing Portal and Supabase or Postgres entitlement sync in Next.js, React and TypeScript apps, verified end to end in Stripe sandbox.
What do you need from me to start, and what should I never send?
Invite me to your GitHub repo (or send a project zip), share the bug steps or plan rules, and provide Stripe sandbox keys only when needed. Please never send account passwords, live Stripe secret keys, Supabase service role keys or real customer card details in chat or in the order form.
My app was built with Lovable, Bolt, Cursor or Replit. Is that fine?
Yes, I fix AI-built billing code every week. AI tools often parse JSON before checking Stripe signatures, skip duplicate-event locks, or leave plan tables editable from the browser. I fix the code cleanly in your GitHub repo so everything syncs right back into Lovable, Bolt or Cursor for you.
What counts as one bug in Basic, and what if my scope is bigger?
One bug is one clear root cause, such as a webhook returning HTTP 400, a broken return URL, or one event failing to update a user plan. If you need multiple fixes or a fresh billing setup, message me first: I check your scope upfront, never add surprise fees, and send a fair custom offer.
Will your Stripe changes break my existing login or live users?
No. I work on a separate Git branch using Stripe sandbox events and spare accounts, never touching live customer records. Before delivery I replay checkout, renewal, failed payment and cancel events, run your TypeScript and production build checks, and show you the before and after proof.
Do you access or store my customers' payment or personal data?
Never. Card numbers stay inside Stripe's own hosted pages, and I verify every flow with sandbox events and spare logins only. I never export, copy or store real user data, keep all secret keys strictly server-side, and delete your local project copy from my computer right after the order.
Do you offer support after delivery?
Yes. If anything I built or fixed stops working as agreed within 7 days of delivery, I fix it at no extra cost. Changes caused by new pricing models, later code edits, other developers or Stripe dashboard edits are not covered, though I am always happy to inspect them first and quote fairly.
What is not included in these three packages?
Stripe account KYC approval, Stripe processing or hosting fees, full UI redesigns, tax or legal compliance advice, and multi-vendor Stripe Connect split payouts are not included in these packages. If you need custom metered usage billing or Stripe Connect, message me first for a custom offer.
How do we switch safely from Stripe sandbox to live payments?
I build and verify every Checkout, Portal and webhook event in sandbox first so zero real cards are charged. At handoff I give you a clear cutover checklist showing which live Price IDs, publishable key and live webhook signing secret you paste into your own host environment variables safely.
Do you also lock down Supabase Row-Level Security on billing tables?
Yes. In Standard and Premium I make sure browser clients cannot edit their own plan or status columns and only verified server webhooks update entitlements. If you want a full database-wide RLS check across your entire app, check out the dedicated Supabase security audit gig on my profile.