Browse categories
Explore
Fiverr Pro
English
$
USD
Reliable Web Development and Cybersecurity Support for Your Projects
GitHub Actions CI/CD pipeline that tests, scans and deploys your app on every push, and blocks the deploy if anything fails.
Most pipelines only build and deploy. I build DevSecOps pipelines, where every push has to clear security checks before it reaches production.
WHAT I SET UP
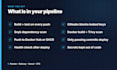
- GitHub Actions workflow: install, lint, test, build
- Gitleaks secret scanning, so a leaked API key fails the build
- Snyk or npm audit dependency scanning
- Docker image build with a Trivy CVE scan
- Push to Docker Hub or GitHub Container Registry
- Deploy to Render, Railway, Vercel or a VPS, pinned to the commit that passed
- Health check that confirms the new version is actually live
WHAT YOU GET
- Workflow files committed to your repo
- Secrets in GitHub Secrets, never in code
- A short guide to reading and re-running the pipeline
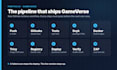
PORTFOLIO: my platform GameVerse ships through this exact pipeline. It runs Gitleaks, Snyk, Docker, Trivy, a gated Render deploy, then an OWASP ZAP scan of the live site.
Send me your repo and where it deploys. I will tell you what it needs before you order.
Does my app need to be dockerized first?
Not for Basic. Standard and Premium build an image, so if you have no Dockerfile yet, order my Dockerfile gig alongside this one, or message me for a combined quote.
Will the security scans break my build?
Only on findings above a threshold we agree on, like critical CVEs. I will not flood you with noise, and I explain every finding I gate on.


