Browse categories
Explore
Fiverr Pro
English
$
USD
DevSecOps Engineer, Kubernetes, Linux Hardening and Firewalls
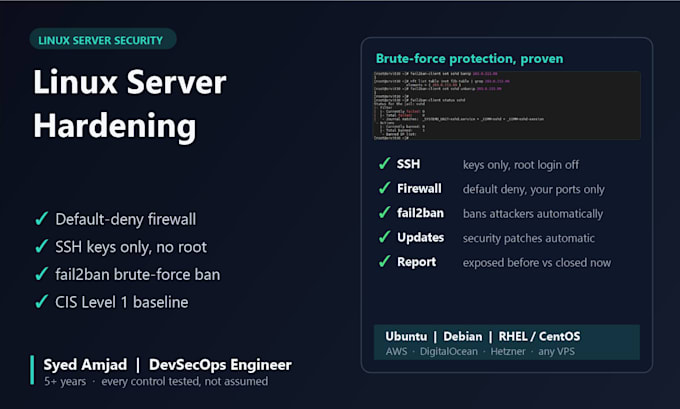
Need a Linux server that is secure from day one, or one that is already exposed to bots? I will set up, secure and harden your Linux VPS or cloud server without locking you out.
What I do:
Every change is backed up and tested first, so your site stays online.
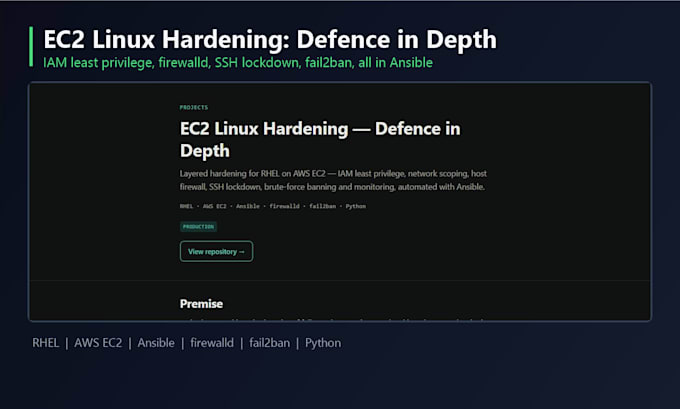
Why me: I built a production firewall automation platform for a large Linux fleet (iptables, ipset, Python, Ansible) with backup and rollback on every deploy. It made deployments 3x faster.
Works with: Ubuntu, Debian, CentOS and RHEL on AWS, DigitalOcean, Hetzner, Linode or any VPS.
Please message me before ordering so I can check your server and suggest the right package.
Server:
Virtual private server
•
Nginx
•
Web server
Operating system:
Linux
•
Unix
Will I lose access to my server during hardening?
No. I keep a second session open, allowlist your IP first, and apply firewall changes with an automatic rollback if the connection drops.
Do you need root access?
A temporary sudo user is enough. You can remove it as soon as the work is done, and I will remind you to.
My server runs Docker. Will the firewall break my containers?
No. Docker manages its own iptables rules, so I filter container traffic in the DOCKER-USER chain and test every published port before handing over.