Browse categories
Explore
Fiverr Pro
English
$
USD
Senior DevOps and Cloud Security Engineer, AWS, GCP, Azure, Kubernetes
Workloads and CI/CD: image and dependency vulnerabilities, supply chain.
What you get
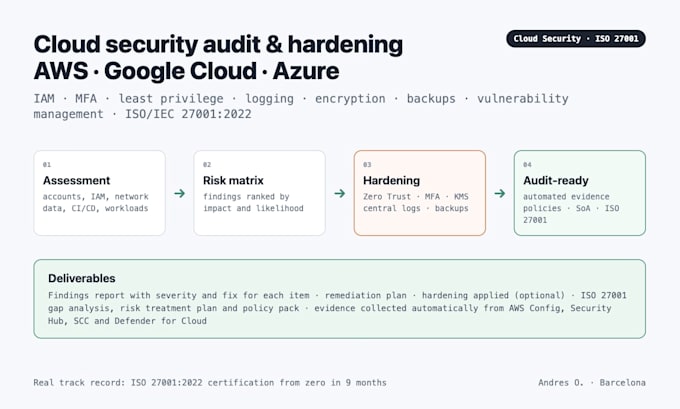
Findings ranked by risk with a concrete fix for each one, a remediation plan and, if you want, the fixes applied. For ISO 27001: gap analysis, risk treatment plan, policies and evidence ready for the auditor.
Track record
ISO 27001:2022 certification from zero in 9 months for a 120-employee software company, 61 of 93 controls evidenced automatically, no major non-conformities.
Senior DevOps & Cloud Security Engineer, 8+ years. Launch prices for my first Fiverr clients.Detection: central logging, alerts, CloudTrail/Audit logs, Security Hub/Defender/SCC.
Data: encryption at rest and in transit, backups and restore tests.
Network: exposure, security groups, public IPs, private endpoints.
Identity: root/owner accounts, MFA, least privilege, keys and secrets.
Find out what an attacker (or an auditor) would find in your cloud, and fix it. I assess and harden AWS, Google Cloud and Azure environments with a Zero Trust approach, and I take companies to ISO/IEC 27001:2022 certification.
What I check
Tools:
Docker
•
GitLab
•
GitHub
•
Kubernetes
•
Amazon EKS
Frameworks:
Terraform
•
Pulumi
•
Ansible
Programming language:
Bash
•
JavaScript
•
Python
•
Golang
•
PowerShell
Expertise:
Installation
•
Migration
•
Configuration
Is this a penetration test?
No. It is a configuration and architecture security assessment; I can recommend a pentest afterwards.
Do you need admin access?
Read-only access is enough for the assessment (SecurityAudit role); hardening needs scoped write access that you can revoke.
Do you sign an NDA?
Yes.
