I will integrate trivy vulnerability scanning into your ci cd

Ukraine

I speak Ukrainian, Russian, English

DevSecOps Engineer

DevOps Engineer and Cybersecurity student with a focus on cloud-native infrastructure automation, GitOps methodologies, and reliable software delivery. I have practical experience building, operating,...
About this Gig

Secure Your CI/CD Pipeline with Automated Vulnerability Scanning

Are you deploying vulnerable containers? Security should not be an afterthought or a bottleneck. I will integrate automated DevSecOps tools directly into your CI/CD pipelines so you can catch vulnerabilities before they reach production.

As a practicing Site Reliability Engineer, I focus on seamless integration. I build security pipelines that developers actually want to use, without breaking your deployment flow.

What I can do for you:
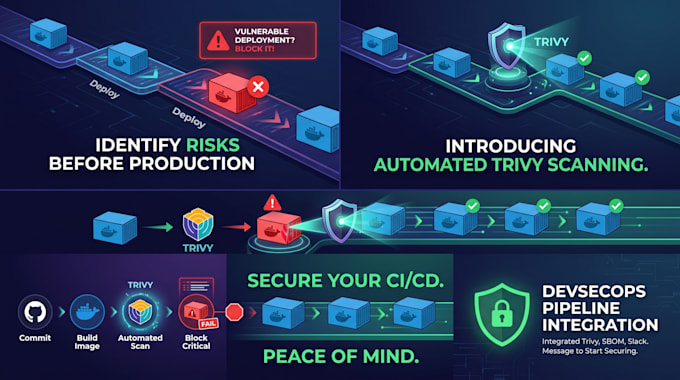
  • Automated Scanning: Integrate Trivy into your GitHub Actions or GitLab CI to scan Docker images, IaC (Terraform), and Kubernetes manifests on every build.
  • SBOM Generation: Automate the creation of Software Bill of Materials (SBOM) using Trivy to maintain transparency in your software supply chain.
  • Instant Notifications: Set up custom webhook integrations to route critical vulnerability alerts directly to your Slack channels.
  • Pipeline Optimization: Ensure security checks are fast and don't block your daily development process.


Tools:

Docker

•

GitLab

•

Jenkins

•

GitHub

•

BitBucket

Frameworks:

Terraform

Cloud Provider:

Amazon Web Services

•

Google Cloud Platform

Programming language:

Python

Expertise:

Installation

•

Development

•

Configuration