Browse categories
Explore
Fiverr Pro
English
$
USD


WordPress runs 40% of the web, which is why it is attacked more than anything else. Out of the box it is wide open. This is the list of things that should have been done on day one.
WHAT I DO
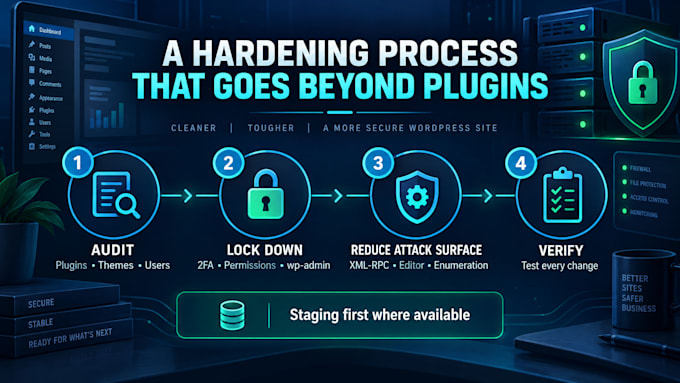
Enforce 2FA on every admin account
Fix file and directory permissions, the number one thing people get wrong
Disable XML-RPC, the file editor and user enumeration
Lock down wp-admin and wp-login with rate limits, and geo rules if you need them
Audit every plugin and theme, and replace the ones with known CVEs
Add security headers and a proper Content Security Policy
Set up backups and actually test a restore (Premium)
WHAT YOU GET
A checklist showing every item, its state before, and its state after. Plus the three things I would do next if this were my site.
I don't just install a security plugin and call it done. Plugins are one layer; most of this list they never touch.
Works on standard WordPress, WooCommerce and multisite. Staging first if you have one.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Website Security Fixes not just scans
Languages
Will my site slow down?
No. Most of this is configuration. Security headers and a firewall usually make the site marginally faster, not slower.
I already have Wordfence or Sucuri.
Good, we keep it and I tune it. A plugin covers maybe a third of this list; the rest lives in config, permissions and the server.
Will anything break?
I test every change. If your site does something unusual, tell me first and I will work around it, on staging wherever one exists.