Browse categories
Explore
Fiverr Pro
English
$
USD
Penetration Tester, AppSec and Cybersecurity Consultant
Is your web application really secure? I test it the way a real attacker would, then give you a clear report your developers can act on.
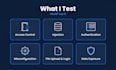
WHAT I TEST (OWASP Top 10)
- Broken access control and IDOR
- Injection (SQLi, XSS, command injection)
- Authentication and session flaws
- Security misconfiguration
- Business logic and file upload issues
- Sensitive data exposure
WHAT YOU GET
- Technical report with screenshots and proof for every finding
- CVSS risk rating and step-by-step fix guidance
- Executive summary for management
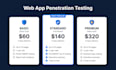
- Free re-test of fixed issues (Standard and Premium)
TOOLS
Burp Suite, OWASP ZAP, Nmap, SQLMap, ffuf, plus manual testing.
ABOUT ME
MS in Information Security, 3+ years of experience, 100+ web apps and APIs tested, former SOC team lead. Certified: eJPT, PEH, Security+.
AUTHORIZED TESTING ONLY
I only test applications you own or have written permission to test. NDA available.
Message me before ordering so we can confirm scope.


Testing application:
Web application
Device:
PC
•
Mac
•
Linux
•
iPhone
•
Android mobile phone
Do you need permission before testing?
Yes. I only test applications you own or have written authorization to test, and I'll send a short scope form before starting.
Will testing break my application?
Testing is non-destructive by default. I recommend a staging environment, and we agree on time windows first.
What does the report include?
Findings with severity, evidence, impact and fix steps, plus an executive summary on Standard and Premium.
Do you exploit vulnerabilities?
Only to prove impact safely, with no data destruction or denial of service.
Is my data confidential?
Yes. NDA available on request, and all test data is deleted after delivery.
Do you test APIs and mobile apps?
APIs that support the web app are included. Dedicated API and mobile testing are separate gigs.


