Browse categories
Explore
Fiverr Pro
English
$
USD
Need an independent security check before a launch, an audit, or a customer security review? I'm an OSCP-certified web application penetration tester and bug bounty hunter. I test your app by hand, the way an attacker would. Not just a scanner report.
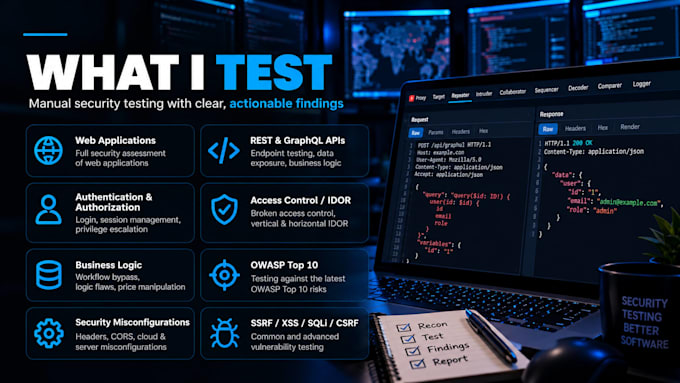
WHAT I TEST (agreed scope only)
HOW I WORK
Recon and attack-surface mapping, then manual testing in Burp Suite, then I validate every finding to remove false positives, then report.
WHAT YOU GET
A report of validated findings with severity, affected endpoint, steps to reproduce, evidence and how to fix it. If I find nothing exploitable in scope, you get a summary of what was tested.
WHO IT'S FOR
SaaS teams, startups, developers, API builders and small businesses.
WHAT I NEED
Target URL, scope, test accounts and API docs (if any).
AUTHORIZED TESTING ONLY
You must own the target or have written permission to test it. No DoS or destructive testing.
Message me your scope first.


Testing application:
Web application
Device:
PC
•
Mac
•
Linux
What do you need from me to start?
The target URL, the in-scope domains or endpoints, test accounts (ideally 2 per role), API docs or a Postman collection if you have them, and confirmation that you own or are authorized to test the target.
Can you test my API?
Yes. I test REST and GraphQL APIs for broken authorization (IDOR/BOLA), authentication flaws, injection, excessive data exposure and rate-limiting issues. A Swagger/OpenAPI file or Postman collection helps me cover more.
Can you test a login-protected application?
Yes, and most serious issues are behind the login. Please provide test accounts. For access-control testing, two accounts per role let me check whether one user can reach another user's data.
Do you provide a report?
Yes. Every order includes a report. Each validated finding has a severity, the affected URL or endpoint, steps to reproduce, evidence and remediation guidance.
Is this manual testing or an automated scan?
It's manual. I may use tools for recon and discovery, but I investigate and validate findings by hand in Burp Suite. You won't get a raw scanner export.
Can you test staging environments?
Yes, and I recommend it. Staging lets me test more thoroughly without risk to production data or real users.
What if you don't find any vulnerabilities?
I don't guarantee findings; that depends on your app and the scope. If nothing exploitable is found, you still get a report listing what was tested, which is useful evidence of your security posture.
Do you need authorization to test?
Yes, always. You must own the target or have written permission from the owner. I won't test third-party sites, and I don't do DoS, destructive testing or anything outside the agreed scope.