Browse categories
English
$
USD
Connect to your AI
Pentester, Offensive Security Engineer, Application Security, Security Developer
As both a Secure Developer and Penetration Tester, I manually audit your source code for exploitable vulnerabilities and deliver clean, working patches that won't break your app.
Automated SAST tools miss business logic flaws and flood you with false positives. I combine deep manual line-by-line review with targeted security analysis across your entire codebase.
Core Review Areas (Including, But Not Limited To):
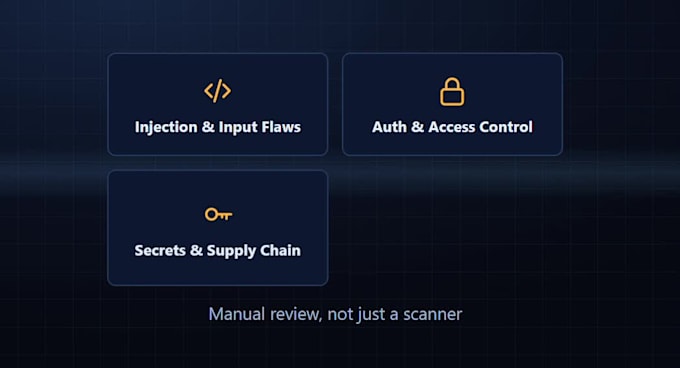
Injection & Input Flaws: SQLi, XSS, CSRF, SSRF, Command Injection, and unsafe deserialization.
Auth & Access Control: Broken authentication, weak JWT/session handling, IDOR, and privilege escalation.
Secrets & Supply Chain: Hardcoded API keys, exposed credentials, and vulnerable third-party dependencies.
Custom Logic & Architecture: Insecure file handling, race conditions, and API/database misconfigurations.
What You Will Receive:
Clear Vulnerability Report with CVSS severity ratings
Exact line numbers & plain-English risk explanations
Clean, production-ready patched code snippets or Git PR
Message me your tech stack and repo size before ordering!

Development technology:
JavaScript
Which programming languages and frameworks do you support?
• • I audit all major backend, frontend, and mobile stacks -- including Python (Django/Flask/FastAPI), JavaScript/TypeScript (Node.js, React, Next.js), PHP (Laravel), Java/Kotlin, C#/.NET, Go, and Ruby. Message me your stack if you want to confirm before ordering.