Browse categories
English
$
USD
Connect to your AI
Splunk SIEM Analyst for SOC Monitoring and Log Analysis
Struggling with Splunk? I will setup your Splunk SIEM and investigate your security logs for you.
I help small businesses, SOC teams, and IT admins get Splunk working properly - not just installed, but actually useful.
What I will do:
- Install & configure Splunk Enterprise / Splunk Cloud
- Onboard data: Windows, Linux, firewall, AWS, Azure, Active Directory
- Create indexes, sourcetypes, and data inputs
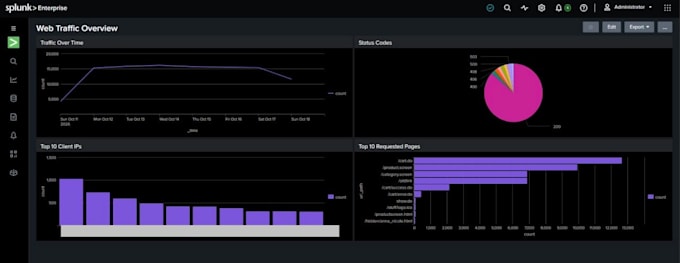
- Build dashboards, reports & real-time alerts
- Investigate suspicious logs, failed logins, malware & brute-force attacks
- Write a clear report: what happened, what is at risk, what to fix
Why me?
I focus on security, not just setup. You get a clean, secured, documented Splunk that your team can actually use.
Message me before ordering if you have a large environment or urgent investigation - I respond fast.
Cloud provider:
Other
Expertise:
Installation
•
Debugging
•
Configuration
Cloud computing resource:
Other
What do you need to start?
Your Splunk access or server details, what logs you want to monitor, and what problem you want to solve.
Do you work with Splunk Cloud?
Yes, I work with both Splunk Enterprise and Splunk Cloud.
Can you investigate a hack / breach?
Yes. Choose Premium. Send me your logs and timeline and I will investigate and provide a full report.