Browse categories
Explore
Fiverr Pro
English
$
USD
Have a frontend built in Next.js or React that needs a real database, authentication, or third-party APIs connected? Generated UI with v0, Lovable, or Cursor and stuck on the backend?
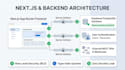
I specialize in building secure, scalable backend architectures and connecting databases for modern Next.js applications.
What I Deliver:
Tech Stack:
Why Choose Me?
Need your frontend connected to a real database? Send me a message, and let's get it running!
Full Stack Web Developer, Modern Framework Specialist
Languages
Can you connect a backend to my v0, Lovable, or AI-generated frontend?
Yes! That is one of my most requested services. You already have the frontend UI, and I will wire up the backend database, user authentication (Clerk/Supabase Auth), and API endpoints so it fully functions.
What is Row Level Security (RLS) in Supabase, and do you configure it?
RLS ensures that users can only access their own private data and cannot view or edit records belonging to other users. I set up strict, production-ready RLS policies on all database tables.
How do you handle database credentials and API secrets securely?
All database connection strings and API secrets are stored strictly in server-side environment variables (.env.local) and called via Next.js Server Actions or Route Handlers, ensuring they are never exposed to the client-side browser.


