Browse categories
Explore
Fiverr Pro
English
$
USD


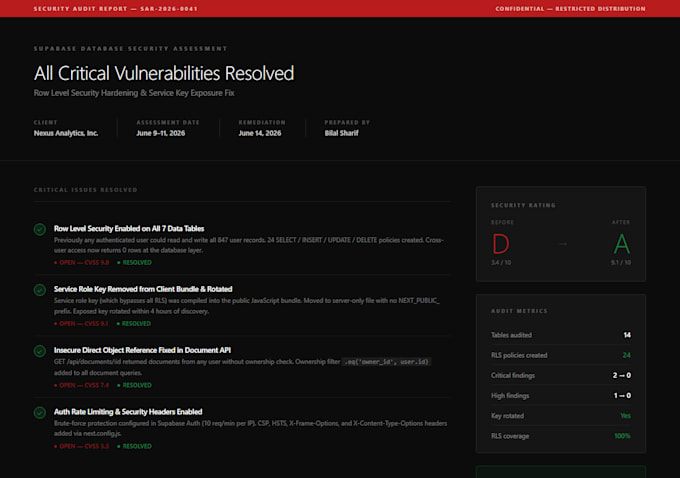
A security audit of your Supabase or AI-built app, done before you launch and get burned. If a tool like Lovable, Bolt or Cursor built it, there is a real chance anyone can read your database right now.
This is not theoretical. In 2025, scans found about 1 in 10 AI-built apps had a critical Supabase RLS hole where the public key let attackers dump every table in under an hour. AI tools ship fast and skip security by default.
What I check and fix:
- Supabase Row Level Security: tables anyone can read or change
- API keys and secrets exposed in your frontend
- Broken or missing authentication
- Users able to see other users' data (BOLA)
- Injection and the OWASP Top 10 issues
- Rate limiting, so nobody can hammer your app
You get a plain-English report of what is exposed and how serious it is, ranked by risk, then I lock it down.
About me: backend and security engineer, years in production, found and fixed a real remote-code-execution bug, and I run systems at over a million requests a month.
Message me your app link or a screenshot and I will tell you how exposed you are.
Fullstack software engineer
Languages
How do I know if my app is even at risk?
If an AI tool built it and nobody checked security, it almost certainly is. The audit confirms it.
I'm not technical.
That's fine. The report is plain English and I do the fixing.
What is RLS and why does it matter?
Row Level Security. Without it, anyone with your public key can read or change your whole database. It's the number one hole in AI-built apps.
Which platforms do you cover?
Supabase and Firebase backends, and apps from Lovable, Bolt, Replit, Cursor and v0.
Can you keep watching it after launch?
Yes, ask about monthly monitoring.