Browse categories
Explore
Fiverr Pro
English
$
USD

Engineering scalable software, APIs, and AI systems
AI CODE SECURITY & ARCHITECTURE AUDIT
THE PROBLEM
Vibe-coded apps built with Cursor, Claude, Lovable, or v0 can contain exposed API keys, weak database rules, prompt-injection risks, and unstable architecture.
THE SOLUTION
We audit your AI application layer by layer to identify vulnerabilities, protect customer data, control unnecessary API costs, and prepare your system for real-world traffic.
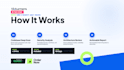
WHAT WE AUDIT
WHAT YOU RECEIVE
A clear security report, prioritized fixes, and step-by-step refactoring roadmap for production readiness.
WHY TKTURNERS
Full-stack AI engineers specializing in React, Next.js, Node.js & mobile applications.
FREE PRE-AUDIT
Message before ordering for a free 5-minute assessment of your app stack.
Development technology:
Python

MEETOVO
Our team developed Meetovo, an all-in-one recruiting platform. We managed the entire project lifecycle, including design, implementation, database management, and deployment, ensuring efficiency, scalability, and a user-friendly experience.
Mar 2022

Empowering Confident Youth
Education Services
Our team developed Empowering Confident Youth, an 11-week program platform for youth development.We managed the project lifecycle, including design, implementation, content integration, and deployment, ensuring an engaging and user-friendly experiene
Dec 2021-Mar 2022
Why should I message you before ordering?
Messaging beforehand allows us to review your tech stack, codebase size, and specific AI builder used so we can recommend the exact package you need and provide a free 5-minute pre-audit check.
Why should I message you before ordering?
We audit code generated by Claude, Cursor, Lovable, v0, Bolt, Windsurf, GitHub Copilot, Replit, and custom LLM coding setups across web and mobile frameworks.
What code access do you need to perform the audit?
You can grant read-only access to your GitHub, GitLab, or Bitbucket repository, or provide a secure ZIP archive of your source code and environment variable schema.
Do I need to cover any third-party tool or API costs?
No. Our audit uses our proprietary inspection toolchains and manual review. You are only responsible for your existing third-party hosting, database, or LLM provider accounts.
What is covered in the Basic Sanity & Security Scan?
The Basic tier scans your repository for hardcoded secrets, exposed API tokens, insecure environment files, critical dependency vulnerabilities, and prompt leakage risks.
Does your audit include fixing the discovered bugs?
The Basic and Standard tiers provide detailed, step-by-step remediation instructions. The Premium tier includes direct hands-on fixes for critical vulnerabilities and architecture bottlenecks.
What format will the audit delivery take?
You will receive a structured PDF report outlining executive summaries, categorized severity levels (Critical, High, Medium, Low), code snippets, and exact fix instructions.
What is your revision policy?
Each tier includes revisions where we clarify findings, re-scan patched code sections, or answer implementation questions to ensure your team can resolve every item.
Can you handle ongoing maintenance or refactoring after the audit?
Yes. If your codebase requires full architectural overhaul, ongoing security oversight, or automated testing suites, we offer dedicated post-audit support and retainer packages.
How do you protect the confidentiality of my codebase and intellectual property?
We treat all client code with strict confidentiality. We never share, publish, or train external models on your proprietary source code, and we delete local copies upon project completion.


