Browse categories
Explore
Fiverr Pro
English
$
USD

Built your app with Lovable, Bolt, Cursor or Supabase and about to launch? AI builders ship fast, but they often leave the boring parts unchecked: database access rules, keys sitting in browser code, and auth settings left on defaults. I review those parts before real users arrive and explain what I find in plain English.
WHAT I CHECK: database access rules on each table · keys and secrets in front-end code · auth settings (sign-up, email confirmation, password rules) · common configuration mistakes for your stack · code review on Standard and Premium.
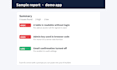
WHAT YOU GET: a report ranked by severity, a clear fix for each issue, and a paste-ready prompt so your AI builder can make the change.
HOW I WORK: only projects you own, with your written permission · read-only access, I never change your live app · your materials are deleted after delivery.
ABOUT ME: I run JonnyLab, a small software studio, have formal cybersecurity training and ship my own apps on Next.js and Supabase.
This is a configuration and code review, not a penetration test, and no review can guarantee an app is free of every issue. Not sure it fits your stack? Message me before ordering.
Security reviews for Lovable and Supabase apps
Languages
Do you need my passwords or admin keys?
No. Please don't send passwords or secret keys. A read-only team invite or an export of your settings and code is enough.
Will you fix the issues for me?
Each issue comes with a paste-ready prompt so you or your AI builder can apply the fix in minutes. The Premium package includes a re-check once you're done.
My app isn't built with Lovable or Supabase. Can you still help?
Message me with your stack before ordering. I'll tell you honestly whether it's a good fit. I mostly work with Next.js, React and Supabase or Firebase back ends.


