Browse categories
Explore
Fiverr Pro
English
$
USD
Licensed U S Attorney, Cybersecurity Incident Response and Data Privacy
When a data breach strikes, delays and regulatory non-compliance result in catastrophic liability, enforcement fines, and brand destruction.
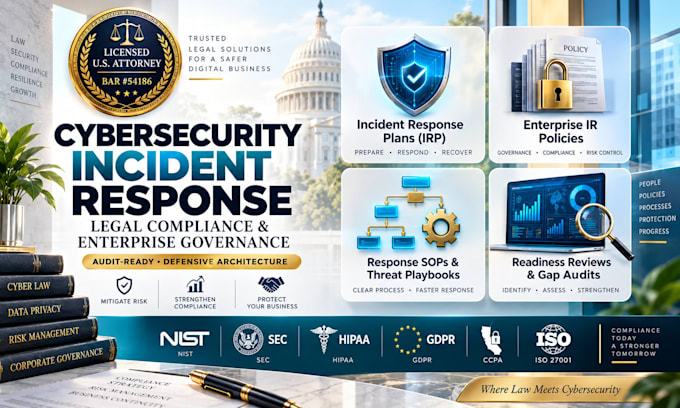
I am Carol Angela Clancy, a licensed U.S. Attorney (Bar #54186). I draft legally binding, comprehensive Cybersecurity Incident Response Plans (IRPs) that protect organizations under state, federal, and global privacy statutes.
What Your IRP Includes:
Off-the-shelf templates fail audits and leave executives exposed to direct liability. Get a verified, attorney-drafted framework tailored to your tech stack and risk profile.
Protect your organization before an incident occurs. Place your order today.
Field of law:
Business (corporate)
Target country:
United States
Please note that there is no screening process for this service. We recommend that you message the freelancer and check all necessary details before placing your order. Pro freelancers in this category have gone through a vetting process. You can find more details here.
How are revisions handled?
Revisions are submitted directly through the Fiverr platform within the package limits to refine technical designations, internal team roles, and governance reporting trees.
How do we tailor the plan to our company’s tech stack?
Upon placing your order, you will complete an onboarding questionnaire detailing your corporate structure, industry, existing infrastructure, data types handled, and compliance obligations.
Can this plan be provided to cyber insurance carriers and compliance auditors?
Yes. These documents are drafted to satisfy strict cyber insurance underwriting requirements, SOC 2 Type II readiness audits, and third-party vendor due diligence requests.
Which regulatory standards does this Incident Response Plan cover?
Depending on your operational jurisdiction, the plan aligns with SEC disclosure rules, HIPAA/HITECH, GDPR, CCPA/CPRA, NYDFS 500, NIST SP 800-61 Rev. 2, and ISO/IEC 27035.
Why do I need a licensed attorney to draft my IRP instead of an IT consultant?
IT teams secure systems, but attorneys protect you from statutory penalties, enforcement actions, and litigation. A legally sound plan safeguards attorney-client privilege, establishes defensible chain-of-custody protocol, and satisfies specific statutory breach disclosure timelines.
