Browse categories
Explore
Fiverr Pro
English
$
USD


Fix your Lovable, Bolt or Replit app's Supabase security and bugs before launch.
In 2025, security researchers found Lovable apps leaking user data because of misconfigured Supabase Row Level Security (RLS). If you built your app with AI and vibe coding, yours could be exposed too.
What I check and fix:
What you get:
Why me: I'm a software engineer with production experience in PostgreSQL, Node.js and Python backends, building secure systems for clients in the USA, Europe and the Middle East, including apps that handle sensitive data.
Works with: Lovable, Bolt, Replit, Cursor, v0, Supabase, Firebase
Not sure if your app is at risk? Message me and I'll do a quick free check of your setup.
Full Stack AI Software Developer
Languages
What is Supabase RLS and why does it matter?
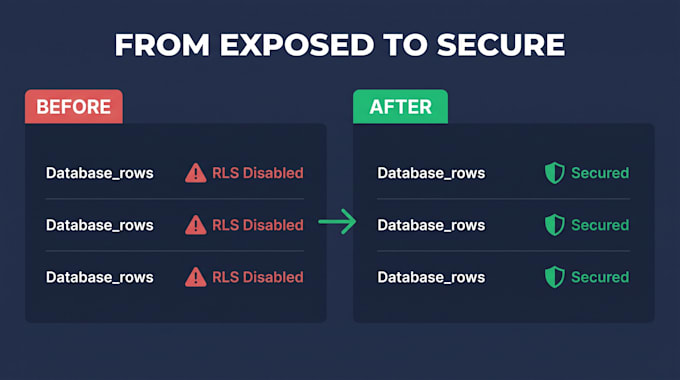
Row Level Security controls which users can read or change each row in your database. If it's missing or wrong, anyone with your public API key can read or delete your users' data.
How do I know if my app is at risk?
If you built it with Lovable, Bolt or Replit and never checked your RLS policies, there's a good chance something is exposed. Message me and I'll do a quick free check.
What access do you need?
Access to your Supabase project (collaborator access is best) and your code (GitHub or a project export). I'll guide you through sharing it safely, and you can remove my access after delivery.
Will you break my app while fixing it?
No. I test every change, and where possible I work on a copy or a separate branch first. Your app keeps working the same way, just securely.
I'm not technical. Will I understand the report?
Yes. The report is written in plain English and explains each issue, the risk, and what I fixed. You don't need coding knowledge.
Can I keep building in Lovable after your fixes?
Yes. I keep your project compatible. I'll also give you simple tips so new AI-generated code doesn't reopen the same security holes.
Do you fix bugs that aren't security-related?
Yes. Standard includes up to 5 bug fixes, such as login problems, broken pages, edge function errors or slow queries. Extra fixes are available as an add-on.
What happens after delivery?
You get 7 days of free support for anything related to my fixes. For ongoing protection, the Monthly monitoring extra re-checks your app for 30 days.