Browse categories
Explore
Fiverr Pro
English
$
USD

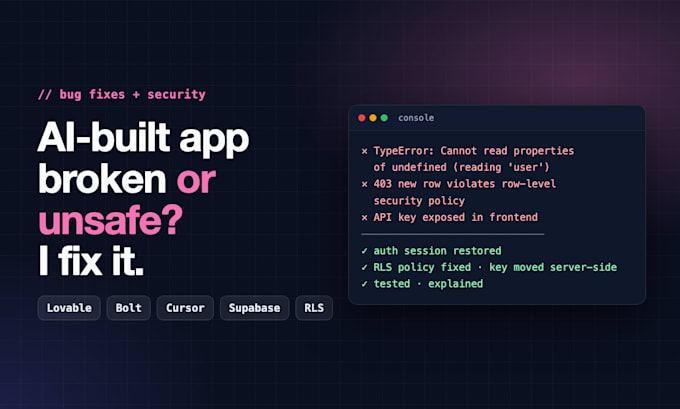
Built your app with Lovable, Bolt, Cursor, Replit or v0 and now it's stuck? Blank screen, broken login, Supabase not saving data? Or not sure it's safe to launch?
I've been writing code since before AI coding tools. I fix the code your AI tool wrote, so you can stop re-prompting, and I look for security holes before hackers do.
What I fix:
- Build, console and Vercel or Netlify deploy errors
- Broken login, Supabase or Firebase issues
- API and Stripe errors, UI bugs
What I check (Standard and Premium):
- Exposed API keys and secrets
- Who can read and edit what: auth, Supabase RLS, Firebase rules
- Premium also: unsafe inputs, file uploads, vulnerable packages
How it works:
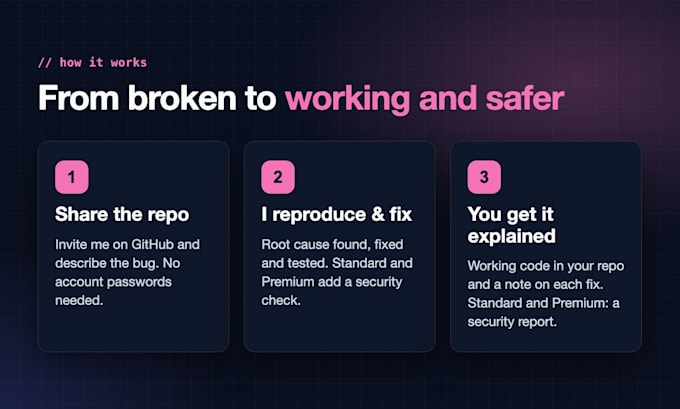
1. Share your GitHub repo and describe the problem
2. I reproduce it, fix it and test it
3. You get working code, a clear explanation and, in Standard and Premium, a security report
Code only: I don't scan or attack live websites or servers.
Stack: React, Next.js, TypeScript, Node.js, Python, PHP, SQL, Supabase, Firebase.
Background: Cisco Networking Academy certificates in Cybersecurity, Networking and Linux.
Not sure which package fits? Send me a screenshot of the error first.
Full stack developer building, fixing and deploying web apps
Languages
What counts as one bug?
A problem you can reproduce with clear steps in something that already exists (e.g. "clicking Save shows an error"). Minor: up to 1 hour of diagnosis. Complex: up to 3 hours. If it needs more, I tell you first. A new, unrelated problem is a new bug; missing features go to my web app gig.
What does the security check include?
Standard: PASS or FAIL report on exposed keys, login and RLS or Firebase rules (up to 10 tables). Fixes are extra. Premium: full audit of up to 20 tables and 15 routes or edge functions, issues ranked by severity with file, line and how to fix. I fix and re-check up to 3 high-risk ones.
Is this a penetration test?
No. I review the source code you share with me. I don't scan or attack live websites, servers or third-party systems. Need your own server set up and secured? See my VPS deploy gig.
Can you guarantee my app is 100% secure?
No honest developer can. I guarantee a careful review of the agreed scope and clear findings you can act on. The check covers the code as it is when I start: a re-check after your own later changes is a new order.
Do you use AI tools?
Yes. I've been programming since before AI coding tools. Today Claude Code and automated scanners read your code and help me work faster, but I make the decisions, check every finding and test every change myself, tracked in git. Prefer no AI? Ask me before ordering for a custom offer.
Do you need my Lovable or Bolt password?
No. Invite me as a collaborator on your GitHub repo: it's the safest and fastest way. I never ask for your main account password. Your code is used only for your order and shared with no one except the AI tools I use (see the AI question). I delete my copy after delivery if you ask.
Will my app keep working in Lovable or Bolt after your changes?
Yes, as long as the project is synced with GitHub. I push the fixes to the branch your tool syncs from (usually main), so they show up in Lovable or Bolt and you can keep editing with the AI afterwards. Database fixes (like RLS) also come as an SQL file with steps to apply it.
What if you can't fix it?
I tell you first if something is out of scope, and offer an extra if a bug needs more time than your package covers. If I can't fix it, you don't pay for it: full refund in Basic; $30 per minor or $90 per complex bug in Standard and Premium, or a full refund if a partial one isn't possible.
Do you work on school or university assignments?
No, I only work on real projects.