Browse categories
Explore
Fiverr Pro
English
$
USD
Full Stack Software and AI Engineer, Apps, APIs, AI Agents, Automation, Security
Before you deploy, or after something went wrong, I read your Solidity contracts the way an attacker would and give you a written report you can act on.
What you get
- Manual line-by-line review of the contracts in scope, plus automated analysis (Slither, static checks, fuzzing where it fits).
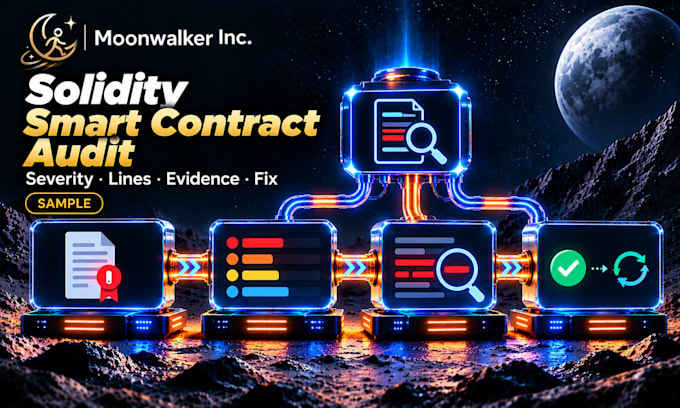
- Findings ranked by severity: critical, high, medium, low, informational, each with the affected lines, how it can be exploited, and the fix.
- Reentrancy, access control, rounding errors, oracle manipulation, front-running, proxy and upgrade mistakes, token standard violations, centralization risk.
- A written PDF report you can show investors, launchpads or your community.
- On the Premium package: a second pass after you apply the fixes, so the report says "resolved".
How it works
1. Send the repository or verified contract addresses and the docs.
2. I confirm scope, lines and price before you order.
3. You get the report and a call to walk through it.
About me: 17 years programming, founder of Moonwalker Inc., a Mississippi software company focused on AI governance and security.
Message me before ordering so the scope is right.


Tools:
Slither
•
OpenZeppelin
•
Etherscan
Cryptocurrency services focus solely on developing and programming. Never share sensitive information or private keys with others.
Which chains and languages?
Solidity on any EVM chain: Ethereum, Base, Arbitrum, Polygon, BSC, Avalanche. Ask about Vyper or Rust contracts.
Is this a certified audit?
It is an independent security review with a written report under my company's name. I state what was reviewed, how, and what was found, and I do not sell approval.
How do you count lines?
Source lines of Solidity in scope, excluding comments, blank lines, tests and well-known libraries like OpenZeppelin.
Can you fix the issues too?
Yes, as a separate order after the report, so the review and the fixes stay independent.