Browse categories
English
$
USD
Connect to your AI
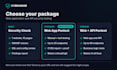
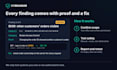

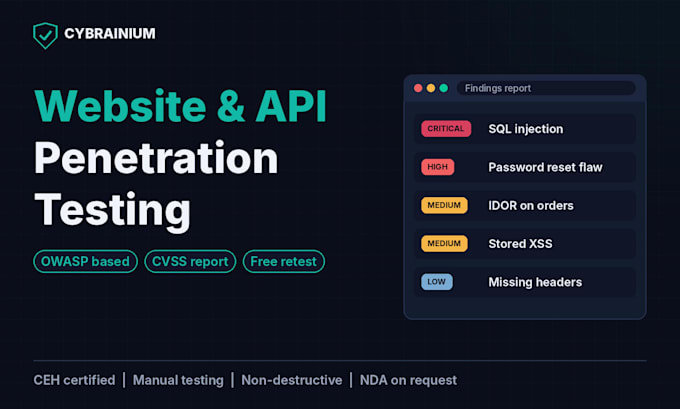
Launching a website or app, or need a security report for a client or auditor? We test your web application and APIs the way real attackers do, then show you exactly how to fix what we find.
What we test:
- Broken access control, IDOR and privilege escalation
- SQL injection, XSS and other injection flaws
- Authentication, session and password reset weaknesses
- API security: authorization, rate limits, data exposure
- Misconfigurations, security headers and SSL/TLS
- Business logic flaws
What you get:
- Manual testing backed by industry tools, based on OWASP
- Every finding verified by hand, no scanner noise
- PDF report with CVSS severity, proof and clear fix steps
- Report format suited for ISO 27001 and SOC 2 evidence
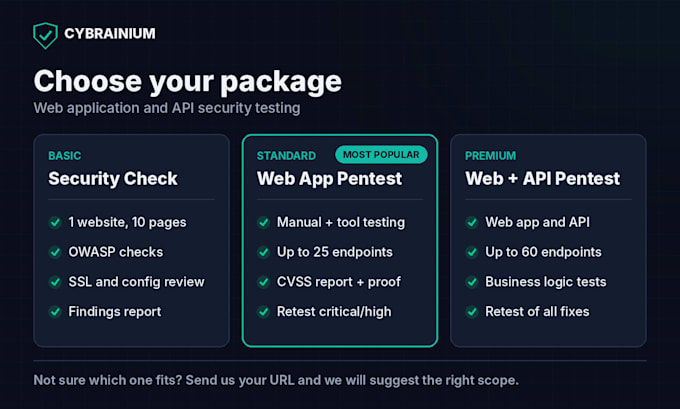
- Free retest of critical and high findings (Standard and Premium)
Why us:
- CEH certified team with bug bounty experience
- Safe, non-destructive testing, staging preferred
- NDA on request
Please message us before ordering so we can confirm scope. We only test systems you own or are authorized to test.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Cybersecurity Services, VAPT, SOC, Cloud Security, GRC, Brand Protection
Languages
Will testing break or slow down my website?
No. We use safe, non-destructive techniques and avoid denial-of-service tests. We recommend testing a staging copy, and we can agree a testing window for production.
What is the difference between a scan and a pentest?
A scan only runs automated tools and gives many false alarms. A pentest adds manual testing, checks business logic and proves each finding. Standard and Premium are full pentests.
Do you need my source code?
No. We test from the outside like a real attacker. For logged-in areas we need test accounts for each user role. Please never share real admin passwords.
Will you test a website I do not own?
No. We only test systems you own or have written permission to test. This protects you and us legally.
What does the free retest include?
After you fix the issues, we test them again and update the report. Standard covers critical and high findings, Premium covers all findings. Please request the retest within 30 days of delivery.
Can you give a letter for my clients or auditors?
Yes. Add the Security assessment letter extra and we will provide a signed summary of the test scope, dates and results.