Browse categories
Explore
Fiverr Pro
English
$
USD
Data Security and Compliance Consultant,GDPR,PIPL,ISO 27001
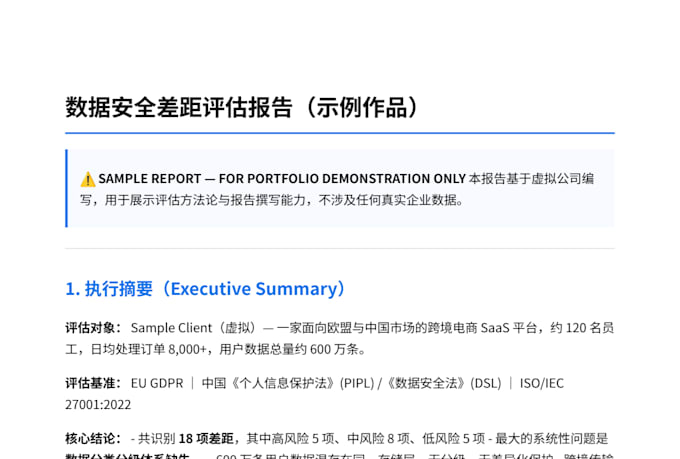
Is your company ready for GDPR, ISO 27001, or China's PIPL? I will run a structured gap assessment and tell you exactly where you stand before a regulator or auditor does.
What you get:
- Control-by-control assessment against 1 framework (GDPR / ISO 27001 / PIPL)
- Risk-rated findings: every gap scored by likelihood and impact
- Remediation roadmap with owners and timelines not a generic checklist
- Data classification framework (L1-L4) on the top tier
How it works:
1. You answer a scoping questionnaire + share existing policies (if any)
2. I assess each control and interview key staff if needed
3. You get the report (PDF) and a debrief call on the top tier
Why work with me:
- I work on both sides of the border: China's PIPL/DSL and the EU's GDPR rare coverage most consultants can't offer
- Audit-style deliverables, not copy-pasted templates: every finding explains WHY it matters and HOW to fix it
- Fast communication in English
- 4 years of hands-on data security experience, CISP-DSG certified
Please note: this is a readiness/gap assessment, not a formal certification audit, and I provide security consulting, not legal advice.

Business type:
Startups
•
SMBs
Industry:
Cyber security
•
E-Commerce
•
Financial services
Is this a certification audit?
No. This is a gap/readiness assessment that shows exactly where you stand against the framework and what to fix before a formal audit. It saves you from failing the real one.
Which frameworks do you cover?
GDPR, ISO 27001, China's PIPL & DSL, and NIST CSF. Pick one per order, or add a second framework as a gig extra.
Do you provide legal advice?
No — I'm a data security consultant, not a lawyer. I assess technical and organizational controls against the framework's requirements.
What do you need from me to start?
A short questionnaire (industry, company size, data types you handle) plus any existing security policies. No access to your systems required for the assessment.