Browse categories
English
$
USD
Connect to your AI
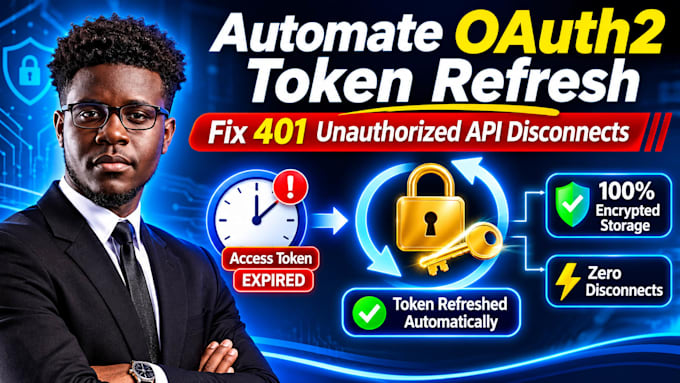
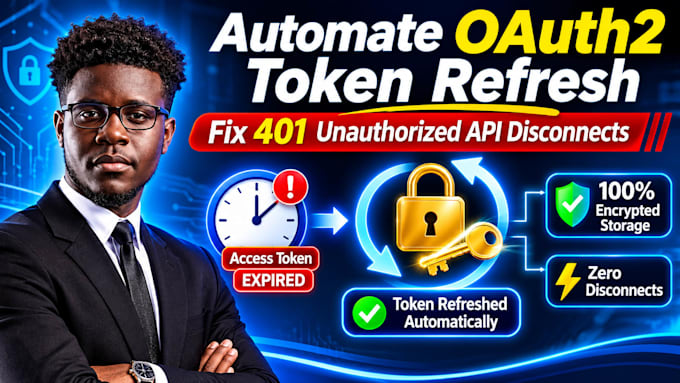
Are your app's third party API connections crashing every hour due to expired access tokens? I build background OAuth2 token refresh handlers that resolve 401 Unauthorized errors permanently.
What I Fix & Build:
How It Works:
Scope Boundaries: Covers OAuth2 token handshakes, refresh engines, and storage logic. Excludes custom single sign on (SSO) portal designs.
Keep your background sync processes running 24/7 without forcing re-logins. Message me with your target API to get started!
Stripe Webhooks LLM Rate Limits Shopify CRM Sync OAuth2 Auth
Languages
Why does my API connection keep failing after 60 minutes?
Most OAuth2 providers expire access tokens after 1 hour. A background engine must use the refresh token to get a new one.
Is it safe to store refresh tokens in my database?
Yes, I implement AES encryption at rest so stored refresh tokens remain secure against leaks.
Which OAuth2 services do you work with?
Google Workspace, QuickBooks Online, Zoom, Xero, Hubspot, and any custom OAuth2 provider.
Will my users ever be forced to re-login manually?
Only if the refresh token itself is revoked by the user or reaches its maximum lifespan (e.g., 6 months).
Can you integrate this into an existing codebase?
Yes, I write modular middleware that plugs directly into existing HTTP client requests.