Browse categories
English
$
USD
Connect to your AI
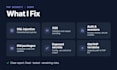

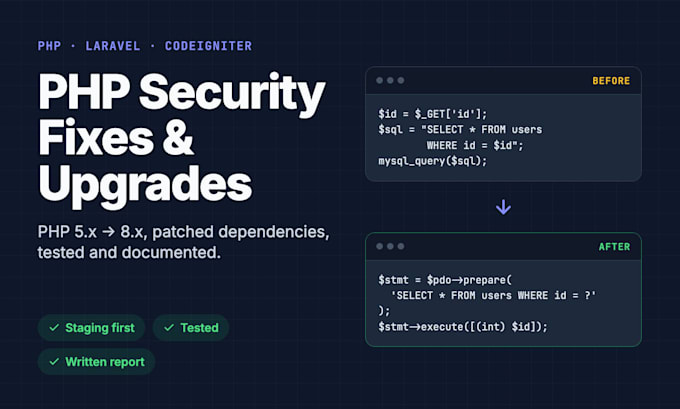
Is your PHP application running on an outdated version, flagged for vulnerable packages, or showing signs of insecure code? I can help you update and harden it safely.
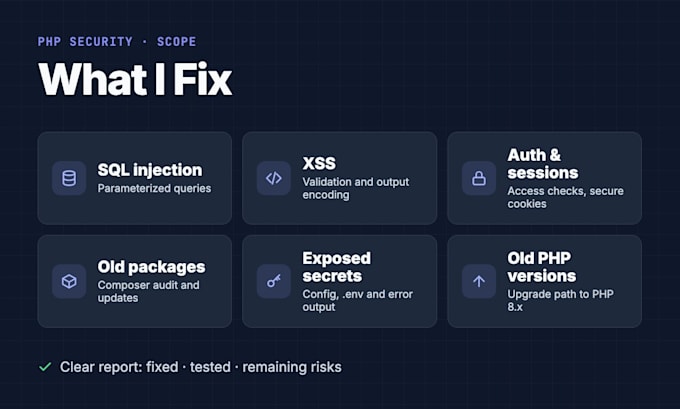
What I can do:
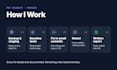
How I work:
Staging and backup first, baseline tests, fixes in small Git commits, then retesting. You get a report of what was fixed, how it was tested, and what risks remain.
Supported: Laravel, CodeIgniter, and custom PHP with MySQL, MariaDB, or PostgreSQL.
Note: scope depends on your code, dependencies, and environment, and is confirmed after a quick review. No one can honestly guarantee an app is 100% secure, but I document exactly what was addressed.
Message me before ordering with your PHP version, framework, and the issue.
PHP and Laravel Security Fixes, Upgrades, and Migrations
Languages
What PHP applications do you support?
Laravel, CodeIgniter and custom (plain) PHP from 5.x to 8.x, with MySQL, MariaDB or PostgreSQL. WordPress isn't my focus, so please message me first.
Can you upgrade an old PHP version?
Yes. I check compatibility, replace deprecated or removed functions, update dependencies and retest. Large jumps such as 5.6 to 8.x may be done in stages and usually need Premium or a custom offer.
Can you fix security vulnerabilities?
Yes, issues I find or that you report (scanner results, CVEs, audit findings), up to your package's item limit. I test and document each fix.
Will my app be completely secure afterwards?
No one can honestly guarantee that. I fix the agreed issues, verify them, and list the remaining risks and recommendations in the report.
Can you work on a live production server?
I strongly prefer staging, and I can help set one up. I change production only with your written approval, a fresh backup and an agreed time window.
Do I get a security report?
Standard and Premium include a written report: findings, changes, tests performed, limitations and remaining risks. Basic includes a change log.
What if an update breaks something?
I test the agreed features before and after. If my change breaks something in scope, I fix it at no extra cost. Every change is a Git commit, so it can be rolled back.
Do you need my passwords?
Never send passwords, keys or .env files in chat. We'll use repository invites, an SSH key you add, or temporary accounts you revoke after delivery.
What do you need before starting?
Your PHP version, framework, hosting details, repository access, known issues, and a staging environment or backup. The order form covers all of this.
Is this a penetration test?
No. This gig fixes and hardens code and configuration you're authorized to change. I don't attack or test third-party systems.