Browse categories
English
$
USD
Connect to your AI
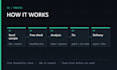

Got a Windows program that crashes, refuses to start, or behaves nothing like its docs?
I dig into the binary, tell you what it really does, and fix it.
What I do:
- Static + dynamic analysis (IDA Pro, Ghidra, x64dbg)
- Unpacking work and the repairs that follow: UPX, custom packers, IAT fixing
- Crash, exception and dependency tracing down to register level
- Legacy repair: runtime, missing DLLs, DPI, OS version problems
- Documenting the logic: functions, checks, file formats, data structures
- Interoperability work on software you own or are licensed to modify
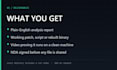
What you get:
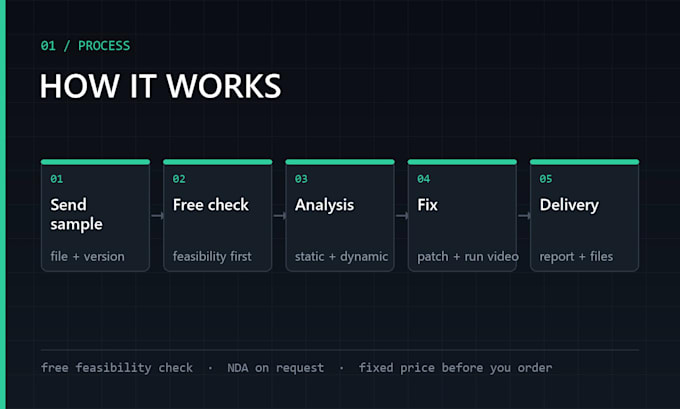
- A plain-English report of what I found
- A working patch, script or rebuilt binary
- A short video proving it actually runs
Send the sample and the version first. I confirm feasibility before you order,
so you never pay for a maybe. NDA on request.
Reverse Engineering Binary Analysis App Security
Languages
Can you work on any software?
I work on software you own or are licensed to use, legacy in-house tools, and repair / interoperability tasks. Send the sample and I confirm feasibility within a few hours, free of charge.
Do you sign an NDA?
Yes, always happy to. Send it over before sharing the files.
What if it turns out to be impossible?
I tell you before you order, so you never pay for a maybe. If it fails after ordering, you get a full refund.
How fast is the first answer?
Usually within a few hours. Delivery starts from 3 days depending on the package.