Browse categories
English
$
USD
Connect to your AI
Software QA Tester ,Beta, Web, App, Game, API and Accessibility Testing
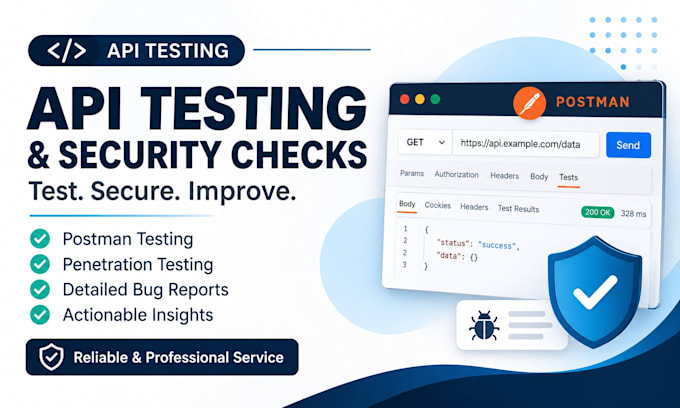
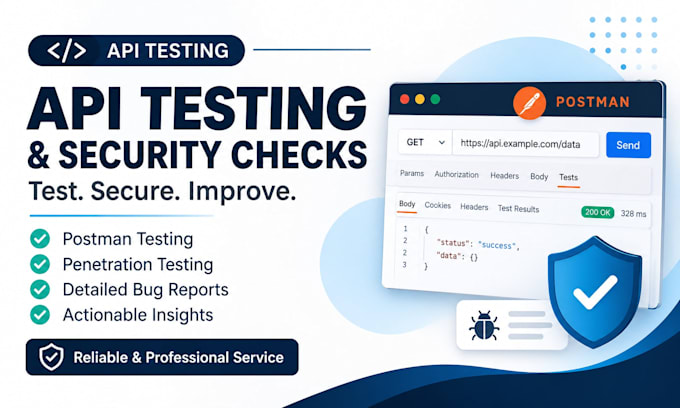
Are API bugs or security weaknesses putting your application at risk?
An endpoint can return the wrong data, mishandle invalid inputs, or expose access-control weaknesses. I help developers and businesses identify issues through structured REST API testing and authorized security checks.
WHAT I TEST
WHAT YOU RECEIVE
WHY WORK WITH ME?
You get organized findings that help your team understand what failed, reproduce the issue, and decide what to fix next.
LET'S TEST YOUR API
Share your API documentation, endpoint count, and testing goals before ordering. Security testing requires explicit authorization and a defined scope. Large projects and advanced assessments require a custom quote.
Testing and reporting only; code fixes are not included unless separately agreed.
Testing application:
API
Development technology:
Java
•
JavaScript
•
Node.js
•
Python
Device:
PC
•
Mac
•
Linux
•
iPhone
•
Android mobile phone
What types of APIs do you test?
I primarily test REST APIs using Postman. Share your API documentation and endpoint details so I can confirm whether your API and requested checks fit the gig.
Do you provide API penetration testing?
Yes, for authorized and agreed scopes. Testing depth depends on the package. Share the target environment, endpoints, and objectives before ordering. I do not test systems without permission.
What do you need to start testing?
Please provide a test or staging URL, API documentation or a Postman collection, relevant test credentials, and the expected behavior of key endpoints.
What will I receive in the final report?
Depending on your package, you receive test results, reproducible findings, expected versus actual behavior, relevant evidence, severity where appropriate, and recommendations for security findings.
Will you fix the bugs or vulnerabilities?
Testing and reporting are included. Code changes, remediation implementation, retesting after fixes, and larger security assessments require a separate agreement.