Browse categories
Explore
Fiverr Pro
English
$
USD
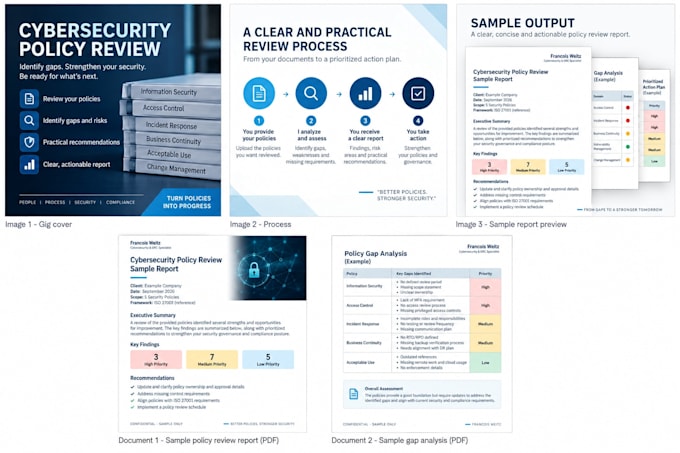
Need a second pair of eyes on your cybersecurity policies?
I will review the policies you provide and identify gaps, weaknesses, unclear responsibilities, outdated sections, missing control requirements, and areas that may need stronger governance or evidence.
Depending on the package selected, I can help with:
This service is suitable for Information Security, Access Control, Incident Response, Acceptable Use, Backup and Recovery, Vulnerability Management, Change Management, Third-Party Security and similar policies.
Important: This is a policy review and gap analysis service. It does not provide certification, legal advice, formal audit assurance or guarantee compliance.
Please remove confidential information that is not necessary for the review before uploading files.


Business type:
Startups
•
Corporates
Industry:
Business services & consulting
•
Financial services