Browse categories
Explore
Fiverr Pro
English
$
USD

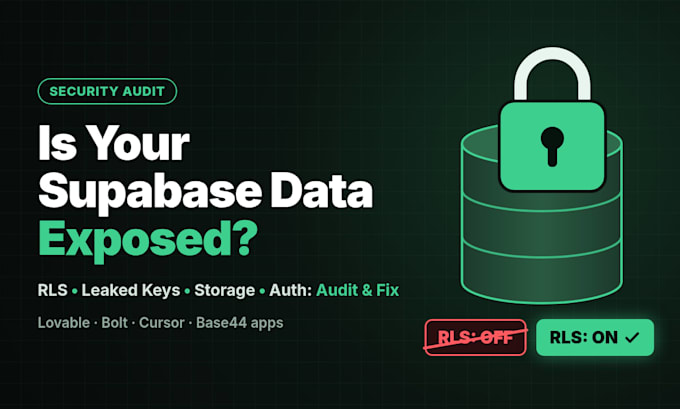
Your Lovable, Bolt, Base44 or Cursor app may be leaking user data: in 2025, CVE-2025-48757 showed 170 of 1,645 scanned Lovable projects had Supabase tables readable with the public anon key. I'm a former sysadmin who runs a Supabase + RLS backend for a 10K+ download app, and I'll audit every table, policy and storage bucket, then fix the holes.
You get a plain-English report (what was exposed, what I changed) and tested RLS policies, with no rebuild and no surprises.
AI tools often ship Supabase projects with RLS turned off, "allow all" policies, public storage buckets, or a service_role key sitting in the frontend. Your app still works fine, but the data is open to anyone.
I'm a former system administrator, and I run Supabase in production for my own app, which has about 5,700 accounts.
WHAT I CHECK
RLS on every table, plus policies that are too broad
Exposed anon/service_role keys in the bundle, repo or env
Storage buckets: public vs. private, upload/read policies
Auth: email confirmation, redirect URLs, open signups
RPC / security definer functions, edge functions
App Launch and Supabase Security Developer
Languages
What access do you need?
I need read access to your repo and a Supabase invite (Developer role) to your project, preferably a staging or branch copy. Please don't send me your personal login.
Will you change my production database?
Only with your OK. I write fixes as SQL migrations, test them on staging or a branch first, and give you a rollback script. Basic is a report only, so nothing gets changed.
Will the fixes break my app?
Tight RLS can block queries that relied on the database being open. I test the main flows (sign up, read and write own data, uploads) after each fix and tell you if any frontend code needs a small change.
My app is built with Lovable / Bolt / Base44. Can you still help?
Yes. Those apps usually run on Supabase underneath, so I work at the database and policy level. If your platform syncs to GitHub, I'll also scan the code for leaked keys.
Is this a full penetration test?
No. This is a focused Supabase configuration audit (RLS, keys, storage, auth, functions), not a certified pentest or a compliance certificate. It targets the issues that most often expose data in AI-built apps.
