Browse categories
Explore
Fiverr Pro
English
$
USD
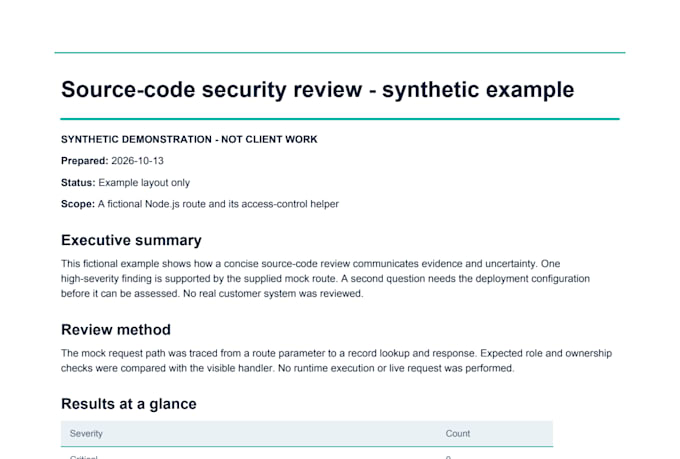
I review buyer-authorized Python and Node.js/TypeScript backend code for security issues. I trace agreed paths through authentication, authorization, input handling, sensitive-data exposure, dependency manifests, and secret handling. You receive a prioritized report with affected files and lines, realistic prerequisites, impact, and practical fixes, plus one 30-minute walkthrough. Scanner leads are investigated; open concerns are labelled separately.
This is a time-boxed static review of your supplied revision, not a penetration test, compliance certificate, or guarantee. No live systems are accessed. Please remove active secrets and unnecessary personal data. Supply an extracted source snapshot and commit/archive hash, exact paths, roles and trust boundaries, and written authorization. Selected source limits: Basic 800 lines/1 flow, Standard 2,500/2 flows, Premium 5,000/3 flows. Repository max 15,000 supported source lines, 1,000 accepted text files, 25 MB accepted text. One revision covers factual corrections on the same revision; new code or fixes need a custom offer. Message before ordering for unusual scope.

Development technology:
Python
Expertise:
Error handling
•
Unit tests
•
Other
What code do you review?
Python and Node.js JavaScript or TypeScript backend applications. The selected paths must fit your package line limit. Ask before ordering for other languages, mobile apps, infrastructure, or large monorepos.
Will you run my app or scan my production site?
No. The standard Gig is a static source review. Any isolated tests require a separately agreed scope and safe environment. Live testing needs separate written authorization naming the target, methods, and time window.
What does the included revision cover?
One round of factual corrections or clarification about the delivered report on the same source revision. New code, new paths, fixes, and retesting require another order or a custom offer.
Can you fix issues found in the review?
Yes, by a separate custom offer after we agree on one finding. A focused patch with a meaningful regression test starts at $250 and adds 3 days; a focused retest of one fix starts at $100 and adds 2 days. Larger changes need a quote.
Will you keep my code private?
Yes. I keep supplied files in an isolated local order folder and do not publish code or portfolio excerpts without your written permission. Remove live secrets and unnecessary personal data before sending the snapshot. AI-assisted source analysis is opt-in.
Do you guarantee that my code has no vulnerabilities?
No. This is a time-boxed review of the agreed revision and paths. The report explains what was checked, what was excluded, and which concerns need additional evidence or testing.