Browse categories
Explore
Fiverr Pro
English
$
USD
Get your Craigslist Ad Designs Now! Get more Clicks
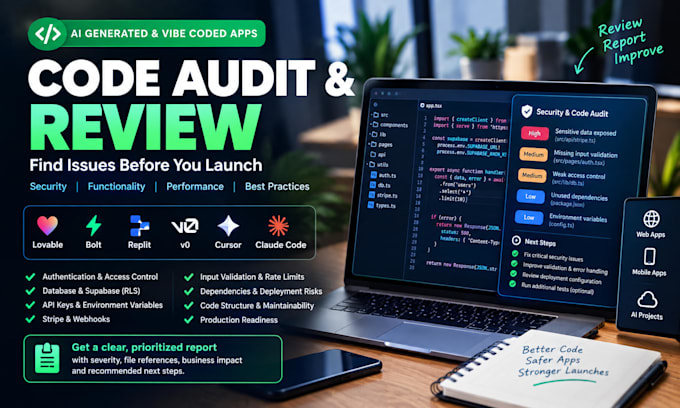
Need a second set of eyes on your AI-generated or vibe-coded app before launch?
I can review your web application code and identify potential issues related to security, functionality, permissions, data handling, and overall code quality.
I can review areas such as:
The review can be applied to apps built with tools such as Lovable, Bolt, Replit, v0, Cursor, Claude Code, or similar platforms.
You'll receive a clear report outlining the issues found, their severity, affected files or areas where applicable, potential impact, and recommended next steps.
Please note: This service provides a code review and recommendations. It does not include code fixes, penetration testing, or compliance certification.
Before ordering, please message me with details about your repository, technology stack, app size, and what you would like reviewed.


Development technology:
JavaScript
What type of apps can you review?
I can review web applications and AI-generated or vibe-coded projects built with platforms and tools such as Lovable, Bolt, Replit, v0, Cursor, Claude Code, and similar technologies.
What areas do you check?
The review can cover authentication, permissions, database access, APIs, secrets, payments, input validation, dependencies, code structure, and other areas relevant to the project.
Will you fix the issues you find?
No. The service focuses on identifying issues and providing recommendations. Code fixes can be discussed separately if needed.
Do you perform penetration testing?
No. This gig is for code review and application assessment, not penetration testing or a formal security audit.
Will I receive a report?
Yes. You’ll receive a structured report describing the findings, severity, affected areas where applicable, potential impact, and recommended next steps.
Can you review a project before launch?
Yes. You can provide your project before launch for a review of the areas included in your selected package.
Do you provide a security or compliance certificate?
No. This service does not provide compliance certification or a formal security certificate.
What access do you need?
Depending on the project, I may need access to the relevant code repository and supporting project information. Never send passwords, private keys, API secrets, or other sensitive credentials through the Fiverr order requirements.