Browse categories
Explore
Fiverr Pro
English
$
USD
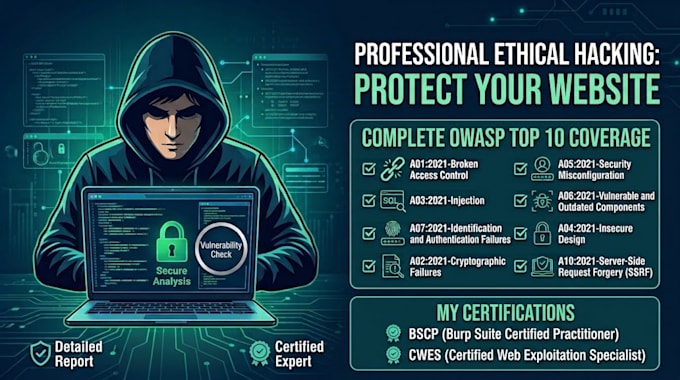
I will test your web application ethically, and with your authorization and give you a report your developers can actually act on.
What I test for:
You always get:
️
Testing is performed only on applications you own or are explicitly authorized to test. Written authorization is required before any work begins.


Testing application:
Web application
Development technology:
.NET
•
HTML & CSS
•
JavaScript
•
Node.js
•
PHP
Device:
PC
•
Mac
•
Linux
Will testing break my site?
I use non-destructive techniques by default.
Which package do I need?
Basic: up to 5 pages or endpoints, no authentication. Standard: up to 15 pages or endpoints, 1 user role. Premium: up to 30 pages or endpoints, 2 roles, includes API.
Do you provide a retest?
Yes, retesting of fixes is included in the Premium package.
Is this legal?
Yes. I only test applications you own or are authorized to test, and I require written authorization before starting.