Browse categories
Explore
Fiverr Pro
English
$
USD
Software Developer and Application Security
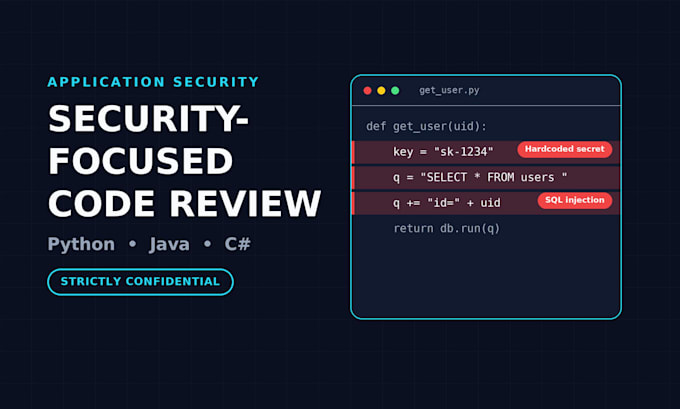
Is your code secure? I'll help you identify potential security issues and improve your application's security.
I provide focused source code security reviews for Python, Java and C# applications.
What I can review:
What you'll receive:
My goal is to provide actionable feedback you can understand and use to improve your code.
Before ordering:
Please contact me with your programming language, project context, approximate source code size, and the files or components you want reviewed.
Your source code will be treated as confidential and handled with care.

Development technology:
Java
Expertise:
Clean Code
•
Other
What programming languages do you support?
Python, Java and C#.
What types of security issues do you look for?
Depending on your application's context, I can review input validation, injection risks, authentication and authorization logic, sensitive data handling, insecure coding patterns, error handling, and other relevant security concerns.
What will I receive at the end of the review?
You will receive a structured review report containing identified findings, relevant code references, descriptions, potential impacts, severity estimates where applicable, and practical remediation recommendations. Annotated screenshots may also be included when useful.
Do you review entire applications or only specific files?
The review scope depends on the package you select. Packages have limits on relevant source code size and file count. Please contact me before ordering to confirm the scope.
Do I need to provide the source code?
Yes. You need to provide the relevant source code files and any necessary technical context.
Can you review code generated by AI?
Yes. AI-generated code can be reviewed using the same security-focused approach as other source code. The review focuses on potential security weaknesses, unsafe assumptions, and implementation issues within the agreed scope.
Will you fix the vulnerabilities you identify?
No, the standard service focuses on identifying and explaining security issues. Implementing fixes is not included, although examples of best practices may be provided in the report.
Can you guarantee that my application is secure after the review?
No. A source code review has inherent limitations and cannot guarantee that all vulnerabilities will be identified or that an application is completely secure. The results depend on the provided code, context, and review scope.
Do you use AI tools to analyze or process my source code?
I do not submit, upload, or share your source code with external AI tools or services. All code reviews are performed manually, ensuring that your proprietary code is not exposed to third-party AI platforms through my review process. Your source code remains confidential throughout the assessment.