Browse categories
Explore
Fiverr Pro
English
$
USD

CyberSecurity Professional
Skills
See my services

SOC Analyst(Management Trainee Officer(MTO))
PTA • Full-time
Sep 2025 - Present • 1 yr
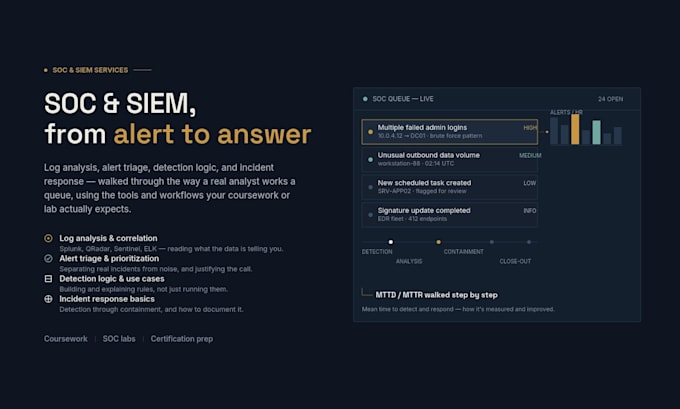
Monitor and triage security alerts in real time using Wazuh SIEM; validate severity, escalate and document incidents per SOC procedures and Incident Response Plan. ● Firewall, EDR, Email Security gateway integration with SIEM and security monitoring. ● Configured and fine-tuned SIEM decoders and log-source integrations to improve parsing accuracy; supported sandbox malware analysis and network threat detection using Suricata/Snort IDS. ● Perform incident handling across MISP, OpenCTI, SOAR and SIRP platforms; analyze logs and IOCs to detect and investigate active threats. ● Investigate network, endpoint and system-level security events to ensure timely detection, containment and response. ● Support threat intelligence operations by collecting, correlating and disseminating actionable IOCs across the SOC team. ● Produce detailed incident reports covering findings, investigation outcomes and remediation recommendations. ● Collaborate with senior analysts to continuously improve detection rules, alert accuracy and incident response workflows.
