Browse categories
Explore
Fiverr Pro
English
$
USD
Web Developer, Cyber Security Specialist, SEO Expert : Nithursan
Level 1
Has met certain performance criteria and shows strong potential in the marketplace.
Highly Responsive
Known for exceptionally quick replies
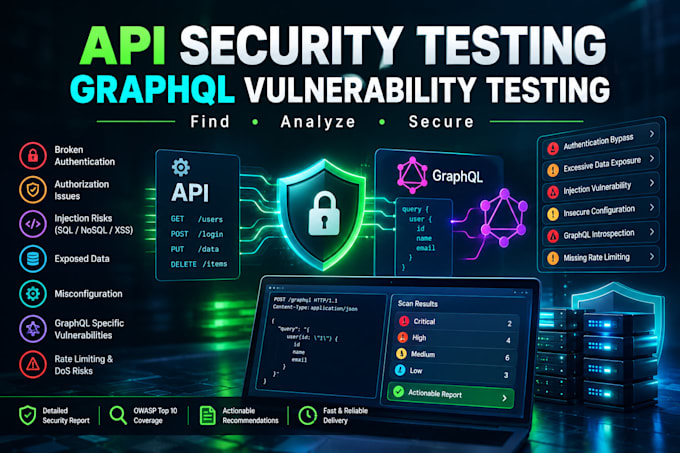
Are your APIs exposing sensitive data? Automated scanners miss the critical, multi-step vulnerabilities that cause real-world data breaches.
I provide expert, manual API Security and GraphQL Penetration Testing to harden your backend against advanced threats. I approach your infrastructure with a bug-bounty mindset, finding the critical flaws others overlook.
My Testing Scope Includes:
What You Get:
Don't wait for a breach. Message me before ordering to discuss your target scope and tech stack.
Testing application:
API
Development technology:
JavaScript
•
Node.js
•
NoSQL
•
Python
•
SQL
Device:
PC
•
Mac
•
Linux
•
iPhone
•
Android mobile phone
What do you need to start the API penetration test?
I need the API documentation (Swagger, OpenAPI, or Postman collection), a list of target endpoints, and valid test credentials with different privilege levels.
Do you test GraphQL specifically?
Yes. GraphQL has unique attack vectors. I test for introspection leaks, alias-based rate limit bypasses, malicious batching, and deeply nested queries that cause resource exhaustion.
Why is manual testing better than automated scanners?
Automated scanners routinely miss business logic flaws and complex Broken Object Level Authorization (BOLA/IDOR) vulnerabilities. Human testers validate results, understand business logic, and adapt attack paths.
What is included in the final deliverable?
A comprehensive Vulnerability Assessment and Penetration Testing (VAPT) report containing CVSS severity scores, precise Proof of Concept (PoC) steps, and remediation guidance.
Can you test my API in a production environment?
es, I use controlled, non-destructive testing techniques under agreed constraints. However, testing in a dedicated staging or QA environment is highly recommended.
Do you check for database injections and client-side flaws?
Yes. I thoroughly test all user-controllable input for database exploitation (SQLi/NoSQLi), complex XSS regex bypasses, and GraphQL injection targeting underlying resolvers.
Will you provide a Proof of Concept (PoC) for the bugs found?
Yes. Every identified vulnerability includes a step-by-step reproduction guide and custom exploit payloads so your development team can easily verify the flaw.
Do you test for Remote Code Execution (RCE)?
Yes. Identifying critical vulnerabilities like remote code execution is a primary focus. I actively analyze endpoints for unauthorized execution paths and systemic server-level flaws.
Do you offer a re-test after we apply patches?
Yes. Depending on the selected package, I offer re-testing to verify that your development team's security patches have successfully mitigated the reported vulnerabilities.