Browse categories
Explore
Fiverr Pro
English
$
USD
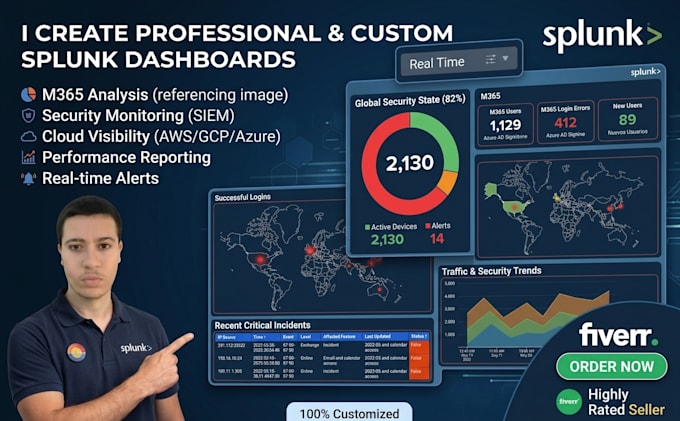
Need help building clean Splunk dashboards, writing complex SPL queries, or setting up reliable alerts? Want to understand how your logs work and learn SPL faster?
I am a SIEM & Splunk specialist. I help clients extract actionable insights from their machine data, detect anomalies with accurate alerts, and master Splunk through clear explanations and structured dashboards.
What I offer:
- Custom Interactive Dashboards: Visually appealing dashboards with dynamic filters, dropdowns, time pickers, and charts tailored to your operational or security needs.
- SPL Query Writing & Optimization: Crafting and troubleshooting queries using commands like stats, eval, rex, lookup, timechart, and transaction for fast search execution.
- Alerts & Scheduled Reports:*Setting up actionable automated alerts with accurate thresholds to keep false positives low.
- Log Investigation & Analysis: Sifting through your event logs to pinpoint errors, security threats, performance drops, or usage trends.
- Splunk & SPL Tutoring / Guidance: Step-by-step walkthroughs to teach you how Splunk works, how to navigate the UI, and how to write your own SPL queries confidently.

Device:
Desktop
•
Laptop
•
Server
•
Mobile
•
Other
Operating system:
Windows
•
Linux
•
Ubuntu
