Browse categories
Explore
Fiverr Pro
English
$
USD
Web Application Penetration Tester and API Security Specialist
Are you sure your web application is fully secure against real-world cyberattacks?
Automated scanners miss critical business logic flaws and broken access controls. With a strong engineering background in full-stack web applications, I perform in-depth manual penetration testing to identify vulnerabilities before malicious attackers can exploit them.
What I Will Test (OWASP Top 10 & Beyond):
Broken Access Control & IDOR (BOLA)
SQL Injection & Command Injection
Cross-Site Scripting (XSS) & CSRF
Authentication & Session Management Bypass
Security Misconfigurations & Sensitive Data Exposure
Business Logic Errors & REST API Vulnerabilities
Deliverables:
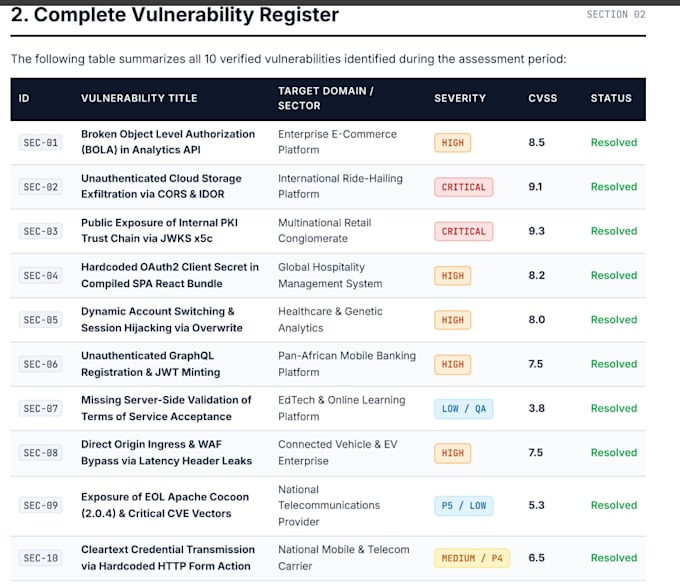
Comprehensive, professional PDF Security Audit Report
Executive summary for management
Detailed technical breakdown with reproduction steps (PoC)
Clear, developer-friendly remediation guidance
Scope & Ethics:
I exclusively conduct authorized security assessments. Please ensure you own or have explicit authorization to test the target system.


Testing platform:
Website testing
Device:
PC
•
Android mobile phone
What do you need from me to start testing?
I need the target URL, scope of assessment, and test accounts/credentials (if testing authenticated user roles). You must also confirm you have permission to authorize testing.
Will the penetration testing disrupt my live website or services?
No. I perform safe, controlled manual testing without aggressive denial-of-service (DoS) attacks, ensuring your production or staging environment remains stable and operational.