Browse categories
Explore
Fiverr Pro
English
$
USD


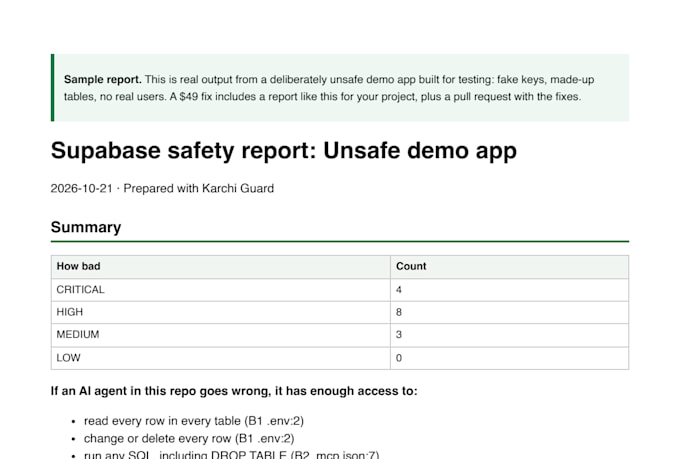
Apps built fast with Lovable, Bolt, Cursor or Claude Code often ship with Supabase data leaks: tables with RLS turned off, policies that let any logged-in user read every row, service keys in the frontend, and AI agents that can drop tables.
I find these and fix them for you.
What I do:
You get: the report, the pull request, and a before/after result.
I will not call your app "100% secure". I tell you exactly what was checked and what was not.
Bigger project (more than 15 tables)? Message me before ordering.
Supabase security and Python developer
Languages
Do you need my Supabase password or keys?
No. I work from your code and schema only. If I find a leaked key, I tell you how to rotate it in your own dashboard.
Will you change my live database?
No. You get a pull request. You review it, merge it, and apply the migration yourself.
My app was built with Lovable. Does this work?
Yes, as long as the project uses Supabase and you can share the code (Lovable can sync to GitHub).
My app says "permission denied for table" since 30 October. Can you fix that?
Yes. That is Supabase's new rule for new tables. I add the grants together with RLS and an owner policy, so the fix does not open your data to everyone.
What if you find nothing?
You still get the report showing what was checked. That is useful proof for you.