Browse categories
English
$
USD
Connect to your AI

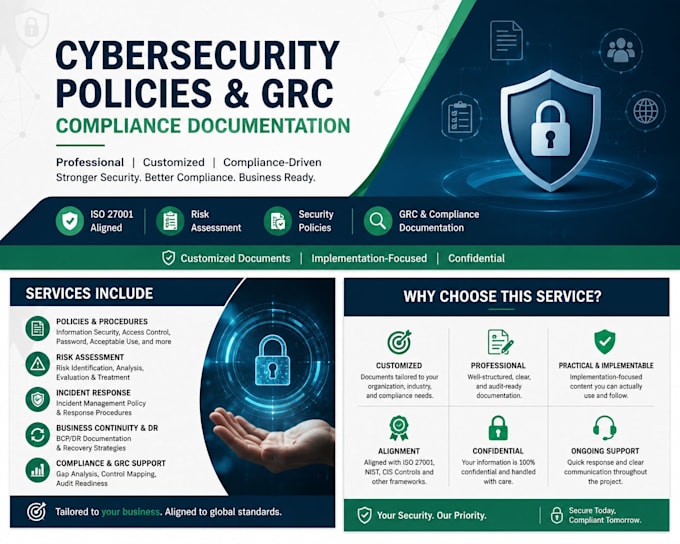

Need clear, professional cybersecurity policies and GRC documentation for your organization?
I provide customized information security and compliance documentation designed around your business requirements and applicable security frameworks.
Services I can provide:
What you can expect:
Every organization has different compliance requirements, so the scope can be tailored to your specific needs.
Please message me before ordering if you require multiple policies, a specific regulatory framework, or a customized compliance assessment.
Cyber Security Analyst
Languages
What cybersecurity documents can you create?
I can create information security policies, procedures, risk assessments, risk registers, incident response documentation, access control policies, BCP/DR documentation, and other GRC and compliance documents based on your requirements.
Can you create ISO 27001 aligned documentation?
Yes. I can develop or review documentation aligned with relevant ISO 27001 requirements and controls. Please share your required scope and existing documentation, if available.
Will the documents be customized for my organization?
Yes. Documents can be customized based on your organization, industry, scope, existing processes, and compliance requirements. I do not rely on a one-size-fits-all final deliverable.
What information do you need before starting?
Please provide the required document or policy name, organization type, applicable framework or regulation, scope, and any existing documents or specific requirements you would like incorporated
Do you guarantee certification or regulatory approval?
No. I provide professional documentation and compliance support aligned with the agreed requirements. Final certification or regulatory approval depends on the relevant certification body, auditor, or regulatory authority.
