Browse categories
Explore
Fiverr Pro
English
$
USD
Full Stack Developer and Security Engineer
You need an external security assessment, and a report you can hand to a client, an investor or an auditor.
WHAT I TEST
- OWASP Top 10, tested by hand and not only by a scanner
- Authentication, sessions, password reset, and the ways around them
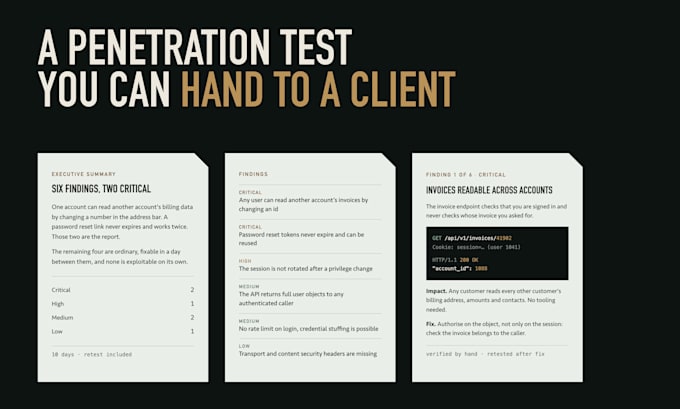
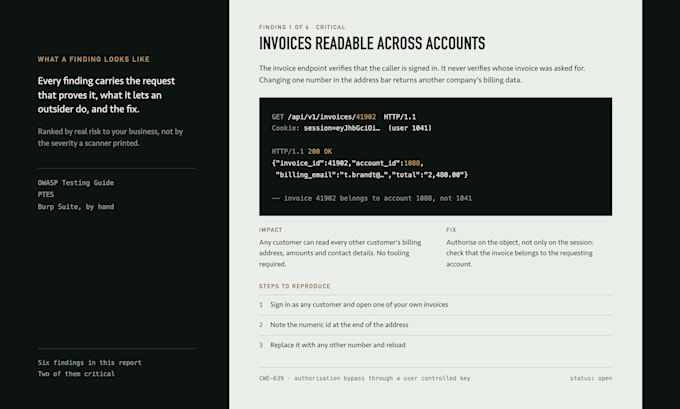
- Access control: whether user A can reach user B's data by changing a number
- Business logic: sequences of legitimate actions that produce an illegitimate result
- APIs, including the endpoints your interface never calls
- Website security configuration: headers, cookies, transport, exposed services
WHAT YOU GET
A report in two layers. An executive summary a non technical person can act on, and a technical section with reproduction steps, evidence and a concrete fix for every finding. Findings are ranked by real risk to your business, not by scanner severity.
RULES I WORK BY
Written authorization from the system owner before anything starts. Agreed scope and agreed testing window. No production data touched, no destructive testing, no denial of service. If you cannot authorize the target, I cannot take the job.
Message me with the target and your timeline and I will tell you what is realistic.


Testing application:
Web application
Development technology:
JavaScript
•
NoSQL
•
Python
•
SQL
•
TypeScript
Device:
PC
•
Mac
•
Linux
•
iPhone
•
Android mobile phone
What do you need from me before starting?
Written authorization from whoever owns the system, an agreed scope, a testing window, and test accounts at each permission level. I do not start without the authorization.
Is this the same as QA or functional testing?
No. Functional testing asks whether the application does what it should. I ask what else it can be made to do. If you need someone to confirm that features work as designed, that is a different service and a different person.
Will testing break our production site?
No. No destructive testing, no denial of service, no production data modified. Where a finding needs proof, I demonstrate it in the safest way that still proves it.
Can you test a staging environment instead?
Yes, and often that is better. It has to be a real copy: a staging site with different configuration produces a report about staging, not about you.
What if you find nothing serious?
You get a report saying so, with what was tested and how. That document is exactly what an enterprise client or auditor is asking you for.
Do you fix what you find?
In the Premium package, yes, working with your developers, followed by a retest and a clean final report. The retest is usually what unblocks a deal.