Browse categories
English
$
USD
Connect to your AI
Web and API Security Testing, CTF Challenge Development
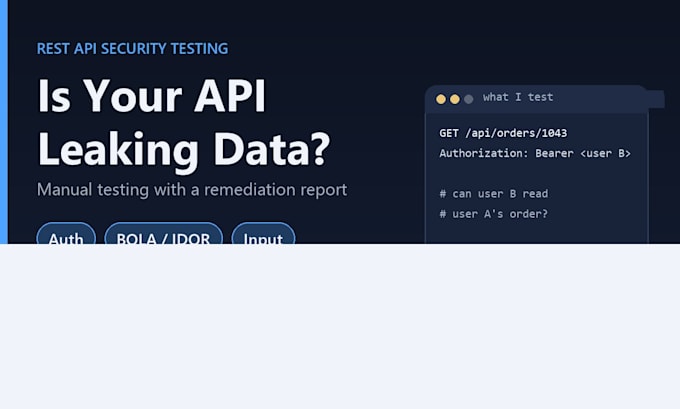
Want to know whether your REST API lets one user read another user's data, or accepts input it shouldn't? I test APIs you own or are authorized to test, and deliver a report your developers can act on.
What I check (depending on the package):
Authentication and token handling
Object-level and function-level authorization (BOLA/IDOR)
Excessive data exposure and writable properties (mass assignment)
Input validation and injection
Security-relevant configuration, e.g. CORS, headers and error handling
These are areas I test, not guaranteed findings.
The Basic package is an automated scan with manual confirmation of the results. Standard and Premium are manual testing.
Every report includes scope and coverage, verified findings with request/response evidence, risk ratings, remediation steps and limitations. Scanner output I couldn't confirm is labelled as unverified.
Scope is counted in endpoints (method + path, e.g. GET /users/{id}) and user roles. Please use a staging or test environment and test accounts. Don't send production passwords in chat.
Not included unless agreed: GraphQL, finding undocumented endpoints, load/DoS testing, fixing code, retesting after fixes.
Device:
Desktop
•
Laptop
•
Server
Operating system:
Windows
•
Linux
•
Ubuntu
Do you test GraphQL?
By custom offer only. Introspection being enabled is a configuration observation, not proof of a vulnerability on its own.
Will you find vulnerabilities?
I can't promise findings. You get the areas tested, any verified issues with evidence, and what wasn't covered.
Production or staging?
Staging or test environments with test accounts are preferred. I don't run disruptive or load tests unless you scope them in writing.
What does a revision cover?
Corrections or clarifications to the delivered report, not testing new endpoints.
Is retesting included?
Yes, with the Retesting After Fix extra. It covers the findings in my original report, not new endpoints.
