Senior Leader in GRC, Privacy, and Cyber Security and Information Risk
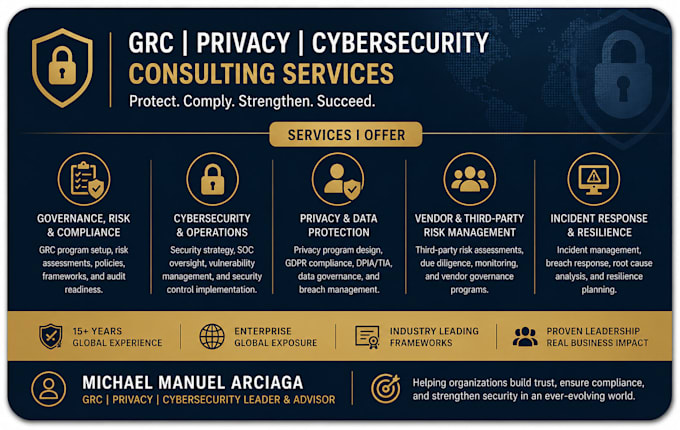
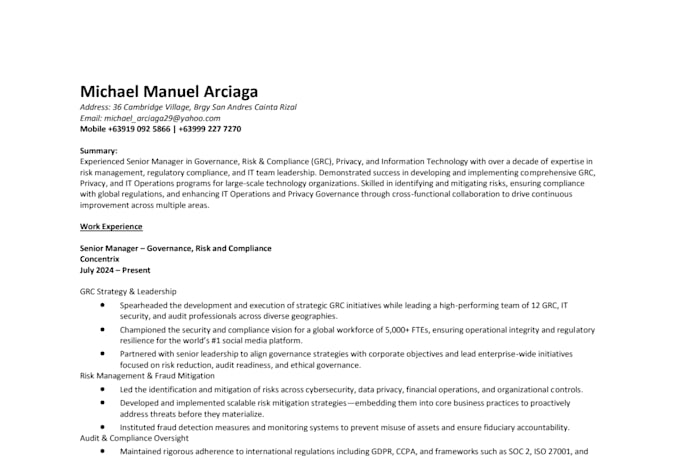
Experienced Senior Manager in GRC, Privacy, Cybersecurity, and IT with over a decade of experience supporting multinational companies, banks, and BPOs. Proven track record in building and enhancing en...
Assess client risks, compliance gaps, security posture, and operational challenges, then provide strategic recommendations aligned with frameworks such as ISO 27001, SOC 2, NIST, GDPR, and privacy regulations.
Lead stakeholders through remediation, incident response, governance improvements, audit readiness, vendor risk management, and security program enhancement to reduce risk and strengthen compliance maturity.
Assess risks, compliance gaps, and security posture, then deliver practical recommendations to strengthen governance, privacy, and cybersecurity programs.
Guide organizations through remediation, audit readiness, incident response, and risk reduction initiatives to improve compliance and operational resilience.
Administration: Manage user accounts, access requests, ticket queues, documentation, and routine system or process administration activities.
Support: Provide first-level technical and operational support by handling incidents, troubleshooting issues, escalating unresolved cases, and ensuring SLA compliance.
Analysis: Monitor alerts, review logs and tickets, analyze recurring issues or trends, and provide recommendations for process or operational improvements.