Browse categories
Explore
Fiverr Pro
English
$
USD
Lead Security Architect for Hybrid Cloud, IAM and Zero Trust
Marlon Costa was selected by the Fiverr Pro team for their expertise.
Vetted for
Cloud Computing
Cybersecurity
Data Governance & Protection
DevOps Engineering
Regulatory Compliance Consulting
Support & IT
Vetted Pro
Your board asked what the risk is worth. Nobody could answer.
Most security reporting gives a board a colour, with no way to tell whether the red one costs ten thousand or ten million.
You are probably here because
What you get
How it works
What you can count on
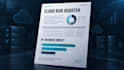
Ranges with stated assumptions, for internal comparison. Never a single invented number.
Works with
AWS, Microsoft Azure, Google Cloud, IBM Cloud, hybrid and on-premises.
Anchored to ISO/IEC 27005, NIST SP 800-30 and FAIR where it helps.
Tell me who is asking and I will say which package fits.


Expertise:
Data protection
•
Gap analysis
•
Risk assessment
Technology:
Cloud - IaaS
•
Data Centers
•
Firewalls
•
Networking
•
Saas
Regulation:
Other
Is this a penetration test?
No. This project is a security risk assessment and architecture review, not an active penetration test. The focus is on identifying risks, control gaps, and improvement opportunities across the scoped hybrid environment.
Which environments can you assess?
I can assess AWS, Azure, GCP, private cloud, on-premises environments, or mixed hybrid scenarios. The project can also include supporting areas such as IAM, privileged access, network exposure, logging, and governance.
Do I need to provide an architecture diagram?
A diagram is strongly recommended because it improves the quality and speed of the assessment. If you do not have one, a written environment summary is acceptable for smaller or well-defined scopes.
What will I receive at the end of the project?
Depending on the package, you may receive an executive summary, findings report, risk matrix, remediation roadmap, and architecture recommendations. The deliverables are designed to be practical and decision-ready.
Is this useful for audit or compliance preparation?
Yes. While this is not a formal certification audit, it is very useful for identifying control gaps, improving readiness, and supporting initiatives related to frameworks such as NIST, ISO, SOC 2, PCI DSS, and similar requirements.


