Browse categories
Explore
Fiverr Pro
English
$
USD
Is your server actually secure or do you just hope it is?
Most servers exposed to the internet are attacked within hours. Open ports, weak configurations, outdated software, unpatched vulnerabilities... I find them before someone else does.
I'm a systems & network engineer specializing in virtualization and security. I will audit your Linux or Windows server and deliver a clear, actionable report not just a scary list of problems.
What's included
What this is NOT
One server. One audit. One revision. Zero marketing fluff just a clear service.
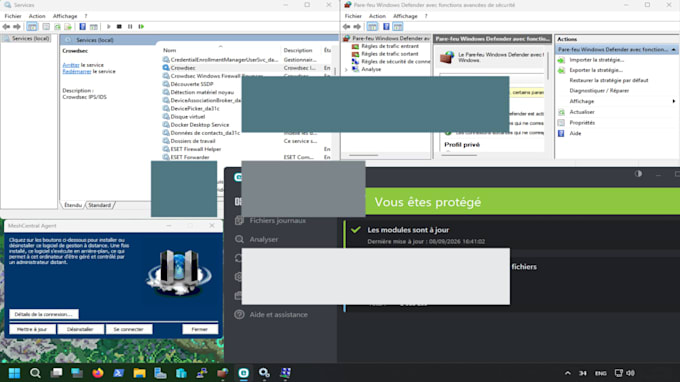
Operating system:
Windows
•
Linux
•
Unix
•
Vmware
•
BSD
Do you need root/admin access to my server?
Yes. A full audit requires root (Linux) or Administrator (Windows) access. I recommend creating a temporary account that you delete after delivery. I never store credentials after the job is done.
Will you modify anything on my server?
No. This is a read-only audit. I observe, analyze, and report. Any changes (firewall rules, updates, hardening) are up to you — or I can help with that as a separate order.
What's the difference between an audit and a pentest?
An audit checks your configuration, services, and known vulnerabilities against security standards. A pentest actively tries to break in (exploitation). This gig is an audit — no exploitation, no risk to your production.
My server hosts client data / is in production. Is it safe?
Yes. The audit is non-intrusive and won't cause downtime. I work during your preferred time slot if needed. However, let me know if any service is fragile so I can adapt my approach.
What does the "1 revision" include?
One round of clarification on the report: rephrasing, additional detail on a finding, or answering your questions. It does not include a new audit after you've made changes — that's a new order.
Can you audit multiple servers?
This gig covers one server. For multiple machines (VMs, clusters, AD environments), contact me for a custom offer — it's often more cost-effective than ordering multiple gigs.
What if you find something critical?
I flag it immediately in the report with clear remediation steps. I don't wait until delivery to warn you about a critical, actively exploitable vulnerability.
Do you audit cloud servers (AWS, Azure, GCP)?
Yes, but only the OS layer. Cloud-specific configurations (IAM, security groups, S3 buckets...) require a different approach — contact me before ordering.
